# AP Cybersecurity
AP Cybersecurity site
# Cybersec progress 9.6.26
======Review so far: =================================
We learned about physical links:
- ethernet cables
- 8 wires in pairs
- on pair is transmit (TX) one is receive (RX)
- full duplex (talking and listening at the same time)
We used terminal to learn about our computer, and to reach out to other computers:
- whoami, last, history, top
- ssh (secure shell), ping, traceroute
- nslookup, dig (names to numbers)
- commands and flags (shutdown -r now)
- privileges: root and sudo
- ctrl-c and ctrl-x (stop and halt)
We learned how to scan a network:
- IP net monitor
- arp-scan
- nmap
We learned about network architecture:
- subnets
- IP addresses
- 192.168.1.x and 10.14.x.y networks
- gateways
- domain name service (DNS)
We need to learn to navigate around the guts of another computer, locally or remotely: why?
- pwd tells you where you are (print working directory) like on a elevator, which floor you are on
- ls tells me what is on that "floor"
- ls -la tells me about even the hidden things on the floor
- ls -lha does all of this in human form
- cd means change directory (floor) on the elevator
Try this:
sudo nano <name> is how we create a file
- in terminal, navigate to your desktop folder
- create a new document called secret: sudo nano secret
- type some secret stuff there
- type ctrl-o (overwrite) and ctrl-x (exit)
- look around your folders for the secret file
- Ok, now repeat the process, creating a file called .hidden (the period makes it hidden)
- type stuff and save
- now look for the file
- ask your friends to find your files by ssh into your machine (don't tell them what you wrote)
to create a new folder (directory) we use mkdir (make a directory)
- try mkdir mystuff (no spaces, computers freak out with spaces)
- cd into that folder: cd mystuff
- make a document there
- ask your friends to find it
- look on your desktop for the folder
- create a hidden file there, see if they can find it
I have hidden a file in another computer, with a reference to yet another computer.
# class notes
Cybersecurity HW-quiz
9.1.26:
enable ssh on your mac
ssh into mac from your pi
ls, pwd, cd, cd ..
sudo nano
ctrl-o, ctrl-x
mkdir
wildcards \*
less, more, cat
ctrl-c (cancel)
ctrl-x (halt)
before——————
ifconfig
arp-a
nmap -sn 192.168.8.0/24
whoami
last
history
hw: 9.1.26
network chuck episode #2
**challenge:**
1. find the machine named victim on the network
2. ssh in
3. list last users and history
4. show who you are
5. create a folder on the desktop in your name
6. create two files: one hidden one visible in that folder with some creative (clean) message
7. find the folder named herobrine
8. read the message and leave a message of your own in a new document
next: 9.1.26 bring headphones
linux for hackers ep02
whoami
cp
mv
rm
cat, less, more
dir structure: bin, sbin, usr->bin, sbin, boot, var, tmp, lib, dev (devices)
/home/User
root user separate in /
adduser or useradd
which (shows which one you are using)
sudo nano /etc/interfaces
gpt: “make me a python game”
————ep03
man pages
what is a terminal? vt100? bit bucket? tty?
OS->shell->terminal
bash, zsh, csh (joke)
ps
powershell=windows shell
$ = user
\# = root
who vs whami
netstat
ps: process
lsof: open files
man = manual pages, space down
ctrl-c
uname -hfor help
apropos usb = keyword search
create python program using ai
solve ssh known\_hosts issue
**9.3.26**
top
htop f9
kill -9
nc -l 1234
scp
sudo apt install
(dpkg next)
pip install xyz --break-system-packages
fastfetch
python3 --version
quiz:
Make sure your laptop is on the elab network for this quiz
You will use the pi for this quiz, and open a text document called "networks" on the desktop with your numbered answers, which you will save on the desktop for me to grade.
Using your pi400 server:
1. there is an intruder on the cyber5 network, find the IP and MAC address for this intruder
2. what brand of computer is this?
3. what “doors” does this intruder have open?
4. how many computers are on this network: 192.168.5.0/24
5. what is the usual router for this network?
6. what would the netmask for this look like?
next:
whoami, who, last, history
DNS and DHCP
nslookup, dig
DHCP leases
basic linux commands:
ctrl-c, z x
pwd, ls, cd
mkdir, sudo nano
ls -la
veda: adev100
leon: 6leon200
tandino: waikii20
rashad: drones34
philip: 99affe
niklas: 99hamburg
ali: scriptkiddie4
8.26.26 homework
1. what does traceroute measure?
2. run traceroute to 8.8.8.8 and describe your results
run the following commands and email your results:
ifconfig
route -n get default
ipconfig getifaddr en0
sudo arp-scan --localnet
nmap -sn 192.168.50.0/24 (change to match the network)
scan a target: nmap 192.168.50.20. (change for target)
deeper scan: nmap -sV 192.168.50.20 (change for target)
sudo nmap -O 192.168.50.20
sudo nmap -sS -sV -O 192.168.50.20
Plan: Q1
- CIA triad
- ethernet cables (the “tubes”)
- connection: 8 wires
- challenge: connection speed-iperf
- compare with fiber, wifi: security, range, speed
- homebrew: linux on owner laptops
- IPNM: gui tool
- terminal: arp -a and nmap -sn 192.168.8.0/24
- challenge: find the intruder
- nmap solo: ports
- challenge: find the doors
- network topology: /24 and /16
- IP address, gateway, subnet, DNS (more on subnet and DNS next)
- MAC address: ID of machine
- challenge: ID intruder
- OUI lookup: who is on what machine
- IPNM: bonjour scan vs address scan (scope)
- back to addresses: test at dorm, home
- ethernet adapters: usb-c for laptops, home scans on wired network: compare
- pi server stations: wifi at first, cyberwifi network (192.168.8.1 with tailscale on glinet)
- challenge: ssh into other machines, then change password (share with me)
- pi scanning tools, gui?
- challenge: scan local wLAN
- navigation: network chuck videos (bring headphones)
- basic commands: ping, traceroute
- navigation: pwd, ls, cd, mkdir, touch, nano, mv, rm
- create hidden file
- ssh challenge: find the file
- navigation: wildcards, up, back, ctrl-cctrl-z
- extended commands:nslookup, dig
- DNS and DHCP, test with IPNM
- python scripts: http server
- setup apache2
- setup network: router, inbound port mapping, AP
- security: MAC filtering
- security: client monitoring
- defense: MAC spoofing, arp cache poisoning
- defense: tcpdump
- defense: wireshark intro-packets
- defend your home project: http, ssh, ftp servers
- firewalls-intro static rules
- SPI firewalls-dynamic rules
- IP addresses → MAC addresses → ports → services → scanning → attack surface
- TCP/IP conversations
- capture, decoding PCAP
- locate, watch, attack
- simple: DDOS
- encryption of traffic
- VPN-truly safe?
- LAN VPN?
- secure web traffic: http vs. https
- content filtering: ad blocking (simple)
- linux tools: Kali linux
- passwords
- hashing
- parrot OS and Kali
- MIM wireless attacks-aircrack-ng
- malware-clam AV EICAR
- log analysis with parrot os
- privacy: VPNs and TOR
- social engineering: internal vs. external vulnerabilities
- social engineering a scammer: [https://www.youtube.com/watch?v=ec57eDghdvM](https://www.youtube.com/watch?v=ec57eDghdvM)
- privacy
- SIM swapping: [https://www.youtube.com/watch?v=64p\_WkYc9d0](https://www.youtube.com/watch?v=64p_WkYc9d0)
Case studies:
1. physical vulnerability: wifi, ethernet, KB, screenlocks, drives, backups
2. LAN security: firewalls, SPI, DPI, uPNP internal holes
3. physical hacking: stuxnet, SCADA
4. prevention: firewall, air gap, defense in depth
5. human: Snowden USB, stuxnet
6. personal: spoofed email, password entropy
7. OSINT: what is available to whom and why
8. LLL analysis of three levels: personal, small shop, enterprise
9. most common attacks: internal vs. external
10. attack detection: log analysis
11. cyberlaw: now and future TGC
12. coding and scripts
13. setup an ad blocker on rPI
14. deep fakes: PBS Hany Farid, C2PA certification
15. cryptocurrency-attacks
16. iot devices-vulnerabilities
17. AI enabled attacks
cybersecurity notes 2026 page
cybesecurity is about protecting your house in a dangerous neighborhood
network: cyber
wifi: cyber
pass: goat8grass\*
(only works on project room east U6lite AP)
Download and install homebrew:
xcode-select --install
/bin/bash -c "$(curl -fsSL https://raw.githubusercontent.com/Homebrew/install/HEAD/install.sh)"
Download and install IPNetMonitor:
[IPNetMonitorX\_2.8c1.dmg](https://elab.hpa.edu/cs/installers/IPNetMonitorX_2.8c1.dmg)
install code:
<?xml version="1.0" encoding="UTF-8"?>
<!DOCTYPE plist SYSTEM "[file://localhost/System/Library/DTDs/PropertyList.dtd](file:///System/Library/DTDs/PropertyList.dtd)">
<plist version="0.9">
<dict>
<key>IPNetMonitorX\_key</key>
<string>2f12c691 ef2c1a46 ed36d1c2 1ad56cfd 27f87fcb 605a3d56</string>
<key>date</key>
<date>2021-09-03T00:00:00Z</date>
<key>licensedCopies</key>
<string>1</string>
<key>name</key>
<string>Bill Wiecking</string>
<key>notice</key>
<string>This file contains a licensed registration code and is Copyright 2002 by Sustainable Softworks Inc.Unauthorized copying and distribution is expressly prohibited.</string>
<key>organization</key>
<string></string>
</dict>
</plist>
Your neighborhood:
IP address=house address on a street
subnet mask=zip code (segments part of the area geographically)
gateway/router=street to highway
DNS (domain name server)=address directory (inside version and outside version)
ports=doors into your house
Who is in your neighborhood?
1. join the cyberwifi (goat8grass\*)
2. arp -a (note the space and the “flag”)
[http://localhost:1313/documents/cybersecurity-notes-2026/cybersecurity-notes-2026/](http://localhost:1313/documents/cybersecurity-notes-2026/cybersecurity-notes-2026/)
class: 8.19.26
quiz:
1. look at your notes, what was your IP, MAC address, subnet mask, dns server and gateway?
2. SCADA is both control and data-why?
finish cables-test
1\. continuity pass/fail
2\. speed
iperf test-speed
repeat to wifi clients-laptops why slower? duplex or simplex?
cyber neighborhood
1. macs with wifi: join cyber wifi (goat8grass\*)
2. find your IP address (option wifi icon)
3. terminal
4. install xcode, homebrew
5. install IPNM
6. who is in my neighborhood? arp -a
7. MAC address and OUI lookup (wireshark page)
8. nmap -sn192.168.4.0/24 (flags again, scope notation)
9. find a random machine, ID by MAC address (mac? pc? vendor?)
10. nmap 192.168.4.x
11. look for ports (doors) on the machine
Homework 8.19.26
Look up your IP address and use IP net monitor to run an address scan on your home network
example: IP address is 192.168.1.12
network scan would be 192.168.1.0/24
this scans 254 machines on your net
Repeat using nmap
example: my IP address is 192.168.1.12
nmap -sn 192.168.1./24
You may have to install homebrew on your mac
We will be using your data next week, so let me know if you have issues with this
Follow these up using arp -a and bonjour scan on IP net monitor
email all of your results before our next class
IPNM (phase one)
1. address scan of the wifi network
2. bonjour scan (like looking at your neighborhood from a drone)
3. DHCP test (leads to network setup)
4. DNS test (leads to nslookup and dig)
pick a pi: This is your server. Keep it alive.
every week we will learn a new attack
This is where you start:
username: pi password: pal82
SSH enabled
HTTP enabled
MQTT enabled
unnecessary service enabled
no firewall
poor permissions
no monitoring
challenge one: who is on my network? (macs: homebrew)
prep: wifi off, LAN on separate network
network scans arp -a nmap -sN 10.14.254.0/16
find host, then nmap host, look for ports
id ports, is it a web server?
can you ssh in?
python script?
IP addresses → MAC addresses → ports → services → scanning → attack surface
hw: scan home wifi using nmap
challenge two: Id the suspect
next: getting out and around
ping, traceroute
navigation: pwd, ls, cd, mkdir, touch, nano, mv, rm
wildcards, up, back
ctrl-cctrl-z
create file: sudo nano, ctrl-o, ctrl-x (exit)
network chuck video?
parts: router-switch-LAN cable, wLAN AP, client
later: DNS-dig and nslookup
syslogd
dhcp
nat
inbound port mapping
Defense:
MAC spoofing
arp cache poisoning
head first networking-pdf
# 9.8.26 notes
**9.8.26**
**You should be comfortable with everything [here](https://elab.hpa.edu/wiki/pages/a2L718H/Module_21_Files_and_navigation.html)**
- MC/FR quiz: exam in a box
- scp python code: laptop to pi
- scp <filename> user@<ipaddress>:/<location>
- mv, cp, rm, cat, less, more
- mv is move, also change name
- cp is copy, from one place to another
- rm is remove, rm -frd removes directories too
- cat, less and more look inside files
- useradd
- **su root**
- **sudo nano /etc/interfaces**
- man pages
- **$ vs # prompt**
- **powershell=windows shell**
- **uname -h for help**
- **apropos usb = keyword search**
- apt install (see below)
- dpkg -i
**wget: installing stuff**
- wget [http://ftp.us.debian.org/debian/pool/main/c/cmatrix/cmatrix\_2.0-6+b1\_arm64.deb](http://ftp.us.debian.org/debian/pool/main/c/cmatrix/cmatrix_2.0-6+b1_arm64.deb)
- ls -lh \*.deb
- dpkg-deb --info cmatrix\_\*.deb
- sudo dpkg -i cmatrix\_\*.deb
- cmatrix
**using apt:**
- sudo apt update
- sudo apt install sl
- sl
**What's the difference?**
- wget → download something from the Internet
- .deb → Debian software package
- dpkg -i→ install a local package
- cmatrix→ run what we installed
- dpkg -L→ see what files were installed
next:[ network structure review](https://elab.hpa.edu/wiki/pages/q0G0N1s/Module_31_Routers_and_firewalls.html)
- permissions
- htop
- firewalls-routers
- tcp/ip stack
- dns
- dhcp
- /etc/host file
- NAT
- inbound port mapping
# Module 0: Cybersecurity course page
Course outline:
Levels:
- Physical: wired and wireless networks, fiber networks-how do they work, how are they vulnerable
- Logical: How does information pass through these networks: protocols, transport, machine to machine communications, malware, hacking, code, operating systems, firewalls, DDos
- Social/Human: vulnerabilities, social engineering, spoofing, digital forensics, phishing
Test cases:
- Stuxnet
- zero day exploits
- cryptography
- botnets
Tools:
- Terminal
- Wireshark
- IPnet monitor
"Writing code itself is useless, but learning system architecture will turn you into a genius" -Matthew Wiecking
1. create ethernet cable, testing, diagnosis, tracking tools
2. sniff wired network
3. compare with fiber (optical) IR cable sniffing
4. wireless contrast-sniffing
5. packets
6. TCP/IP conversations
7. capture, decoding PCAP
8. locate, watch, attack
9. simple: DDOS
10. advanced: FTP vs. SFTP
11. encryption of traffic
12. VPN-truly safe?
13. LAN VPN?
14. secure web traffic: http vs. https
15. protocols, ports
16. firewalls: block doors, burglar example
17. SPI: stateful packet inspection: http vs https
18. content filtering: ad blocking (simple)
19. platforms: pi, laptop, desktop, server
20. hardware
21. OS options: mac, windows, linux
22. linux deep dive: file structures, permissions
23. linux tools: Kali linux
24. social engineering: internal vs. external vulnerabilities
Course Description:
This course introduces students to the fundamentals of cybersecurity through interactive activities, real-world case studies, and hands-on labs. Students will learn how to stay safe online, understand how cyberattacks work, and explore careers in cybersecurity. The course builds critical thinking, ethical awareness, and technical confidence using both unplugged and online tools.
Course Objectives:
- - Understand the core principles of cybersecurity (confidentiality, integrity, availability)
\
- - Identify different types of cyber threats and attacks
\
- - Practice safe online behaviors and password hygiene
\
- - Explore ethical hacking and digital forensics
\
- - Learn about network security, cryptography, and firewalls
\
- - Investigate career paths in cybersecurity
[https://cybersecurityguide.org/resources/cybersecurity-101/](https://cybersecurityguide.org/resources/cybersecurity-101/)
Essential skills:
- spotting phishing-email headers-create PSA for HPA
- domain names-why do you need to know these?
- How filters work
- How MFA works-weaknesses, hacks
- [https://cybersecurityguide.org/resources/phishing/](https://cybersecurityguide.org/resources/phishing/)
- DNS attacks: Starbucks example MIM attacks
- [https://github.com/farhanashrafdev/90DaysOfCyberSecurity](https://github.com/farhanashrafdev/90DaysOfCyberSecurity)
## Additional migrated files
Files present in the Apple export but not embedded in a page:
- [Download Screenshot 2025-08-20 at 4.06.53 PM.png (image/png, 1.9 MB)](https://bookstack.kamuela.org/attachments/322)
- [Download Screenshot 2025-08-26 at 3.49.09 PM.png (image/png, 61.8 KB)](https://bookstack.kamuela.org/attachments/323)
- [Download Take Control of Your Wi-Fi Security (1.7).pdf (application/pdf, 1.4 MB)](https://bookstack.kamuela.org/attachments/326)
- [Download Take Control of Your Online Privacy (5.1).pdf (application/pdf, 2.5 MB)](https://bookstack.kamuela.org/attachments/330)
- [Download Take Control of Your Online Privacy (5.1).pdf (application/pdf, 2.5 MB)](https://bookstack.kamuela.org/attachments/333)
- [Download Take Control of Your Online Privacy (5.1).pdf.zip (application/pdf, 2.1 MB)](https://bookstack.kamuela.org/attachments/334)
- [Download server\_https.py (text/x-python-script, 965 B)](https://bookstack.kamuela.org/attachments/335)
- [Download Take Control of Golden Gate (1.0).pdf (application/pdf, 2.0 MB)](https://bookstack.kamuela.org/attachments/341)
- [Download Take Control of iOS 27 and iPadOS 27 (1.0).pdf (application/pdf, 3.4 MB)](https://bookstack.kamuela.org/attachments/342)
---
Migrated from Apple Server Wiki. Original page ID: q6h4d9q
# Module 1.1: Ethernet cables
- If you want to learn about driving, you first have to understand what a road is.
- In this case, network "roads" are cables, but can also be fiber optics or wireless networks
- We need to understand how to create one of these "roads" from scratch
- We will be using either category 5 "cat5" or category 6 "cat6" cables
- cat5 has a max speed of 1 gb/s, especially if it is labeled cat5e, or cat5 extended
- cat6 has a max speed of 10 gb/s
- The cable ends for these are not interchangeable, as one wire is a bit thinner than the other (cat5 is 24AWG while cat6 is 23AWG, a bit thicker)
- The ends are called RJ45 and has 8 slots
- When viewed with the flat side towards you, these are the colors:
[Download O O G BI BI G Br Br.tiff (image/tiff, 429.6 KB)](https://bookstack.kamuela.org/attachments/321)
- This is NOT random
- The first two orange pairs (1 and 2) are for data transmit
- The green pairs (3 and 6) are for data receive
- The blue pair is for power over ethernet (POE) plus (+)
- The brown pair is for POE negative (-)
- This color is different from 8 conductor (4 pair) telephone cables which may look exactly alike
- Reason? Phone cables start with 4-5 as line one, then 3-6 as line two, 2-7 as line three and 1-8 as line four
- Each of these has up to 90 volts on each pair (when a telephone rings) so we separate our color code for computers
- Reason? Plugging a computer into a phone outlet will not burn out the network card on the computer this way
---
Migrated from Apple Server Wiki. Original page ID: V6c8B7u
# Module 1.2: Terminal commands, network scanning
9.1.26: terminal commands
Reference:
[Download Take Control of the Mac Command Line with Terminal (3.4).pdf (application/pdf, 2.2 MB)](https://bookstack.kamuela.org/attachments/329)
We will be using macbook air computers, with OS version 12.7.6 on the elab network wifi. IPNM was version 2.7.3 or 2.8c1
terms and commands to know:
- whoami
- last
- history
- ping
- traceroute
- ssh
- say (mac only)
- shutdown -r now
- sudo
- IPnet monitor
- TCPdump
- DOS and ddos
- flags
- ctrl-c and ctrl-z
- wifi pulldown on mac to determine network info and signal strength
- whoami: who are you logged in as. first step in detecting hacking incidents on your computer, the command who does the same thing
- last: the last users logged in
- history: the last commands that were issued on your computer, good for tracking invasion, but also for recording notes on your work
- ping: just like it sounds, sends a small packet (ICMP, more on this later) and records the time in milliseconds to return to you. useful for seeing if a machine at an IP address is active, hidden or far away
- traceroute: traces the path to the website or computer. boring if you are all in the same room, but exciting if you want to know why COD is so slow where you are. it records each step of the path in milliseconds
- ssh: secure shell, how you get access to the terminal on another machine. in our lab, we all know the login for others' computers, so we can login and look around. this can be used multiple steps, e.g. you can login to John's computer then ssh over to Mary's computer, and Mary will think John is attacking her.
- say: loads of fun, makes the remote computer say what you type. use the -v flag (more on flags next) to change voices
- shutdown: tells the computer to shutdown. useful in the format shutdown -r now, meaning shut the computer down, restart, and do it now. one can also add time like shutdown -r +600 which is ten hours from now, to cover your tracks
- sudo: treat me as "root" or god on the computer for this command. used to do commands that are blocked. really not a good idea to login as root on any computer unless you know what you are doing. it is possible with root access to erase your entire computer, or to create hidden files, cover your tracks, install malware and so on. rootkits are software packages to gain root access on a remote computer, doing these things
- IPnetmonitor: an excellent GUI (graphical user interface) for many of these commands
- TCPdump: a "dump" of all traffic on the network, useful for diagnosing issues, or to see invasions
- DOS: denial of service, sending many pings at once, called a "ping flood attack" overwhelming the remote computer. a dDOS is a distributed attack using many computers at once
- flags: after a command, there is a space, then a hyphen (dash) where one can add a letter to make the command to special things, for example ping -f means run ping and "flood" the victims computer. shutdown -r means reboot after shutting down.
- ctrl-c (stop) and ctrl-z (halt): control-c is a common stop command, or cancel, to halt (less gentle) use ctrl-z
- wifi pulldown menu: shows connection strength (RSSI) and connection speed (RX and TX). useful for diagnosing wireless issues and network status (router, IP address, subnet mask)
Fun challenges:
1. scan our local network, find one of our laptops, remote login
2. make the laptop say something
3. show that you are logged into the computer from their terminal
4. remotely reboot their computer (with permission)
8.19.25:
- resources, icloud, apps
- nmap and arp-scan from terminal (using brew)
- wireshark demo
- FTP password demo using tcpdump -i en0 port 21 (setup server on victim machine)
- wireshark demo using web traffic
- nslookup demo
- subnets and IP addresses
- 10.14.253.0/24 network
- NAT for internal servers (e.g. home)
- DNS and dig
8.21.25:
port scan
service ports:
21 FTP (file transfer protocol)
22 ssh (secure shell)
80 http (web)
138 smb (windows file sharing)
443 https (secure web)
82 (web alternate)
8080 (web proxy)
ARIN.net and nslookup
stealth mode on macs
ping proof
email headers-find sender
browser tracking-disable
8.26.25
pwd: where am I?
ls: list the files where I am
cd: change my directory
IP Net monitor:
address scan: 10.14.253.0/24 in the elab
bonjour scan: printers
connections: watch what your computer is connecting to
DHCP lease: when you got an address, when it expires
DHCP test: test the local server for speed, and if there is a rogue server present (2 will show up)
DNS lookup: names to numbers, you can specify which server is answering, internal or external
Interface info: useful for detecting errors or collisions
Link rate: test link speed to a server
Ping: like it sounds, link to a device
Port scan: scanning for ports or "doors" on a host
Subnet calc: really useful in setting up addresses on a network
TCPdump: dumps entire conversation into your computer
TCP info: useful for setting up your web servers
Traceroute: traces the path to a server
cb52f155-5158-5158-1f64-f762f81e63a3
---
Migrated from Apple Server Wiki. Original page ID: v94988R
# Module 2.1: Files and navigation
======Review so far: =================================
We learned about physical links:
- ethernet cables
- 8 wires in pairs
- on pair is transmit (TX) one is receive (RX)
- full duplex (talking and listening at the same time)
We used terminal to learn about our computer, and to reach out to other computers:
- whoami, last, history, top
- ssh (secure shell), ping, traceroute
- nslookup, dig (names to numbers)
- commands and flags (shutdown -r now)
- privileges: root and sudo
- ctrl-c and ctrl-x (stop and halt)
We learned how to scan a network:
- IP net monitor
- arp-scan
- nmap
We learned about network architecture:
- subnets
- IP addresses
- 192.168.1.x and 10.14.x.y networks
- gateways
- domain name service (DNS)
We need to learn to navigate around the guts of another computer, locally or remotely: why?
- pwd tells you where you are (print working directory) like on a elevator, which floor you are on
- ls tells me what is on that "floor"
- ls -la tells me about even the hidden things on the floor
- ls -lha does all of this in human form
- cd means change directory (floor) on the elevator
Try this:
sudo nano <name> is how we create a file
- in terminal, navigate to your desktop folder
- create a new document called secret: sudo nano secret
- type some secret stuff there
- type ctrl-o (overwrite) and ctrl-x (exit)
- look around your folders for the secret file
- Ok, now repeat the process, creating a file called .hidden (the period makes it hidden)
- type stuff and save
- now look for the file
- ask your friends to find your files by ssh into your machine (don't tell them what you wrote)
to create a new folder (directory) we use mkdir (make a directory)
- try mkdir mystuff (no spaces, computers freak out with spaces)
- cd into that folder: cd mystuff
- make a document there
- ask your friends to find it
- look on your desktop for the folder
- create a hidden file there, see if they can find it
I have hidden a file in another computer, with a reference to yet another computer.
Your challenge is to find the files.
---
Migrated from Apple Server Wiki. Original page ID: a2L718H
# Module 9.1: C-I-A and the cybersecurity "kill cycle"
CIA is not just a secret branch of the government, it stands for three key parts of cybersecurity:
1. Confidentiality: making sure what you store on your computer is not shared (data)
2. Integrity: making sure your data is not changed in any way, e.g. a bank balancee
3. Accessibility: making sure you can access the data, e.g. ransomware
Look up ["cybersecurity kill cycle"](https://www.lockheedmartin.com/en-us/capabilities/cyber/cyber-kill-chain.html)
Seven steps to breaking into a computer or network:
1. recon: network scanning, ports (burglar looking around your house for open doors or windows)
2. weaponization: create a weapon that can use these ports (doors, use a key or a brick?)
3. delivery: deliver the weapon (send the code into the machine, burglar into your house)
4. exploitation: execute the weapon (start up the code, burglar takes stuff)
5. installation: setup back door or reverse connection (burglar fixes a window so they can get in later)
6. command and control: cover your tracks, take over the machine (go in later to get more)
7. actions: delete data, insert data, copy data for extortion, lock files for ransomware (get your stuff)
**Unavailable Apple Wiki media:** the exported data did not include file bd61e9af-650e-4fd5-adb7-fa0dba8df476.
---
Migrated from Apple Server Wiki. Original page ID: c3u5t4
# Module 1.3: Cyberchallenge #1: networks
Email your answers to
You may use the notes on the weblog, as well as the web to complete your evil task...
1. Using the tool of your choice, find the IP address of several of your classmates' computers
2. Ping these and record your results
3. With permission, make their computer say your name
4. Lookup a company on the internet and record their IP address
5. Ping this company
6. Do a trace route on this company
7. When is your DHCP lease due to expire?
8. Find the linkrate to another computer in the room
9. Run a port scan on the computer at 10.14.88.83
10. Is this running a web server?
11. What other services (names, not ports) is it running?
12. Who was the last person to login to your partner's computer?
13. ssh into the computer at 10.14.88.83 (pi, papaya77)
14. create a folder on the desktop with your name, no spaces
15. navigate into that folder (see the weblog for notes on this)
16. create a document with a secret message
17. challenge your classmates to find the message
18. repeat the process, only this time, name your document starting with a period: .secret
19. look on the desktop of the 83 machine, look inside the folder, can you find the document? why?
20. On your own computer, using terminal, create a folder on your desktop, with both a visible and an invisible file in it.
21. to view a file in terminal, use the command less, e.g. less filename
22. using the commands in the weblog, find the hidden herobrine file I've hidden in the machine called pi-delta (you will have to find the IP address)
23. login to pi-delta and cd to /var/www/html
24. open a browser and go to 10.14.88.83
25. look at the text on the web page
26. using sudo nano, change the words "Apache2 Debian Default Page" into something more interesting
27. ctrl-o and ctrl-x to save your edits
28. look at the web page now. congratulations, you have successfully hacked a website
---
Migrated from Apple Server Wiki. Original page ID: S4w6q5z
# Module 3.1: Routers and firewalls
Review:
We know how to scan a network to see who is on the network ("homes"), which doors are open ("ports") and how to get into them via ssh to change things inside the home (sudo nano).
We need to learn how to protect these ports, using a firewall.
Let's review the network architecture:
Internet terms:
- Your computer needs 4 things to be able to get onto the internet:
- IP address, example 10.14.88.83
- Subnet mask, example 255.255.0.0
- Gateway/router, example 10.14.1.3
- Domain name server (DNS), example 10.14.1.4
Here's what each one does:
IP address:
All traffic on the internet or local area network (LAN) is in the form of packets of information, like mail envelopes with a letter inside. Each letter you mail has two important things: the address you want it to go to, and the message inside the envelope.
- TCP/IP is the format of these, which stands for Transmission control protocol and internet protocol.
- The TCP part is the message, and the IP part is the envelope, with an IP address on it.
- Check the IP address of your machine:
- From the GUI: open system preferences, network
- From the terminal: type ifconfig
- Your computer may have an address in the form 10.14.253.x, this means you are "leasing" an address from the system (more below)
Subnet mask:
- Imagine you want to stay in one of two large 254 room hotels. One has long hallways, and very few floors, the other has many floors, but short hallways.
- If you want to sleep, you don't want many people walking down the hall in front of your room. You want many floors with fewer rooms per floors.
- This is what subnet masking does on a network. Each of the four segments can hold 254 addresses.
- At home, you probably have a network that looks like this:
- IP: 192.168.1.49
- mask: 255.255.255.0
- router: 192.168.1.1
- dns: 192.168.1.1
This means that the last zero can hold up to 254 addresses (from 192.168.1.1 to 192.168.1.254)
- HPA has this sort of mask:
- 255.255.0.0
- which means that
- 10.14.0.0
- is the elab, which can have 254 x 254 addresses
- It makes for a quieter network, also providing some security as others cannot see you easily.
Router/gateway:
This is the gateway for all of your traffic, usually the access point at your home. The technical difference between these words is that a router routes traffic between two networks of the same type (like ethernet), while a gateway is between different types of networks (like a cable modem or DSL gateway).
A firewall is just a gateway that has an outside part and an inside part.
Your gateway may also distribute IP addresses inside your network. At home this will likely look like 192.168.1.x, where at the elab, our network leases addresses in the form 10.14.253.x.
To scan these addresses here, you can use nmap 10.14.253.0/24
Domain name server:
- This is the computer on your network or outside that translates names into numbers, like a digital phone book.
- Try this in terminal:
nslookup elab.hpa.edu
1. when you get the address, write it down
2. open a browser
3. go to elab.hpa.edu
4. now go to the numbers you wrote down.
5. Try this with another name, either on campus or off
6. you are asking our domain name server (DNS) to resolve the name into a number
7. this also works in reverse, from numbers to names
8. using ARIN.net you can find the location of IP addresses outside your network
----tools to use to check your network configuration, or fix a broken one-------
NSLOOKUP:
- Say you want to find out the name of something, or the IP address from the name.
- try this:
- nslookup
- (you will get a funny > sign)
- type:
- server 10.14.1.4
- type:
- elab.hpa.edu
- what do you get?
- where is this machine?
- Try again using 8.8.8.8 as the server (this may be blocked by our system)
The best use of this is to find out what OTHER people might call a machine.
- We have several DNS servers at the elab, the main one is at 10.14.1.4
- Others to try:
- 4.4.4.4
- 8.8.8.8 (google)
- you can get out by typing
- exit
- or control-z (halt)
Ping and traceroute:
- Imagine you want to find out if a machine is responding (you can block this by using "stealth mode")
- In terminal ping one of the IP addresses in your class
- ping an address out on the internet
- what is the difference?
now try this:
traceroute www.apple.com
- It should give you a trace of the path your connection took.
- Try this with other addresses on and off campus.
-----------------------
A firewall is a device that physically separates two networks. If the firewall is inside your network it can be called a router.
Both terms mean the same thing, we just use firewall to indicate there is an outside and an inside.
You will setup a firewall here, and your friends will try to "break in".
Remember from our burglar metaphor, the windows and doors that are open-a firewall is like a fence around your house, with a gate that allows you go to get your mail and send mail, get the newspaper, but no strangers should be able to visit without your permission.
Router setup:
We will be using the TP-Link Archer C9 home router/access point for your network.
Why? It should be similar to most home routers you will setup for yourself or your friends.
Industrial ones for colleges and such may have more options, but the fundamentals are the same.
Here's what it looks like:
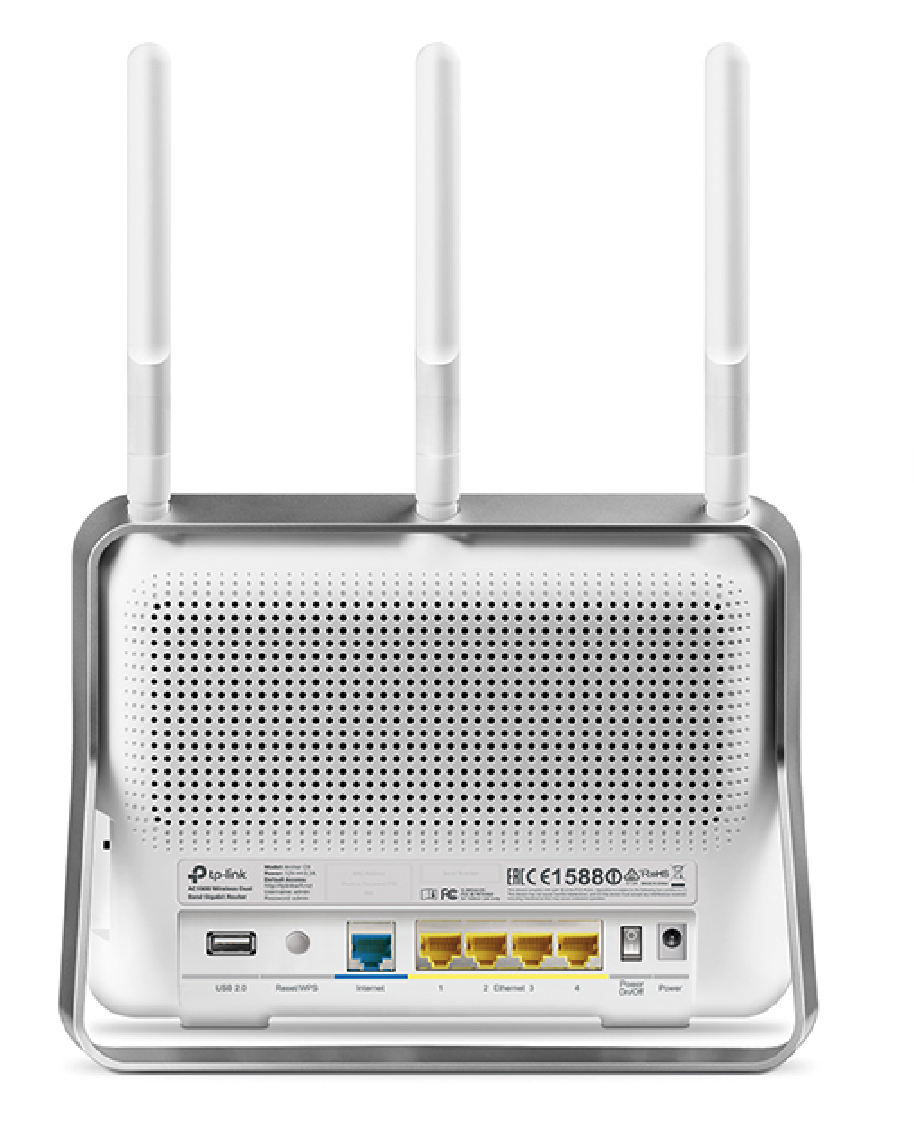Screenshot 2025-09-03 at 4.37.41 PM.png
- start with the ports: blue is the WAN (wide area network) you connect to the internet
- yellow are the LAN (local area network) ports for your network.
- the usb port is for external storage
---
Migrated from Apple Server Wiki. Original page ID: q0G0N1s
# Module 3.2: Cyberchallenge #2: router setup
router-gateway challenge
1. setup your router with an external address in the form 10.14.90.x and write this on the board
2. setup a LAN network with internal network scope 192.168.6.1 with 254 hosts
3. connect one of the pi400 to your LAN using an ethernet cable
4. find the IP address for the pi400 inside your network
5. use the DHCP setting to give it a fixed address
6. the pi has a web server built in on port 80, setup inbound port mapping (forwarding)
7. challenge your neighbors out in the cruel internet to view your web page
8. enable port forwarding for ssh and challenge them to get into your pi 400 and create a folder with their name on it and a hidden message inside that folder (optional)
9. close off ssh access when you are done and create a hidden wifi network
10. disconnect the pi 400 from the ethernet and connect to your access point using wifi on the pi 400
11. use access controls to block the pi then unblock it using MAC address filtering
12. do the same for your laptop, blocking by MAC address
13. use content controls to block a named site for the pi 400 and test
14. use timed access to enable then disable the pi 400 on the wifi network
15. challenge your neighbors to find your wifi network based on name using our lab macbooks (the new thin ones) or your laptop (apple silicon)
16. enable a guest wifi network and see if anyone can join that
17. after they record the MAC address of your access point, challenge them to find your hidden network using the same MAC address
18. on the lab macbooks, use wifi scanning tools to scan the elab wifi networks
19. go on a wifi hunt around the campus looking for wifi networks
20. map out coverage areas using the lab macbooks
21. search for access points and identify the vendor from the MAC address (DO NOT BREAK IN)
22. record the MAC address for car wifi units, and use OUI lookup to determine the vendor
---
Migrated from Apple Server Wiki. Original page ID: K3h1o6Q
# Module 9.2: stuxnet and zero day attacks
cybersecurity notes: first massive "kinetic attack" impacting machinery
[https://elab.hpa.edu/cs/videos/zero%20days.mp4](https://elab.hpa.edu/cs/videos/zero%20days.mp4)
- 00-21:00 cyber background
- 21:00-38:00 what are centrifuges, how the code will be used
- 38:00- 57:00 cyber command, NSA, governments
- 57:00- NSA hackers
terms:
- airgap
- C2
- SCADA
- PLC
- zero day exploit
- DLL
questions:
1. what is a zero day exploit?
2. how did they know the code was from a nation state not a hacker?
3. what is a digital certificate?
4. why is learning about PLCs so important? (Arduinos are PLCs)
5. was there a C2 element in Stuxnet?
6. why were gas centrifuges so important?
7. did they just destroy these, or was it more complex?
8. did the operators know what was going on?
9. why was this important to the malware attack?
10. what is yellowcake uranium?
11. what is it turned into, and for what?
12. if you have seen Top Gun: Maverick, what is similar?
13. How did the PR film the Iranians made help to identify the code?
14. Look at the “balloon code”-do you see anything like the arduino code?
15. Why is it so scary to link code to “real world physical destruction”?
16. What is a DLL in the windows operating system?
17. What is the 4th dimension of warfare, according to the film?
18. What is the NSA?
19. What was buckshot yankee?
20. Compare the NSA use of remote computers with botnets
21. Why are password lists that have not been used before also known as "zero day" lists?
---
Migrated from Apple Server Wiki. Original page ID: 0115t5h3
# Module 4.1: Wireless scanning
Let's start with your wifi connection.
you already know how to hold option and the apple signal to get data, try the iwifisignal app installed on the elab macs:
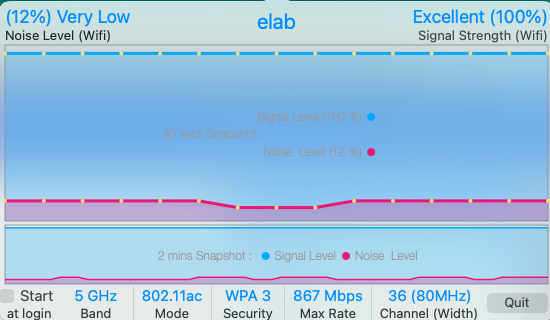Screen Shot 2025-09-10 at 11.18.18 AM.png
What do you see here that you don't see elsewhere?
What are the different levels of security? WEP, WPA, WPA2, WPA3?
What are the physical bands?
Try scanning with your own (newer) laptop, or look under "about this Mac" to see what other bands your laptop is capable of using.
Next try wifi explorer:
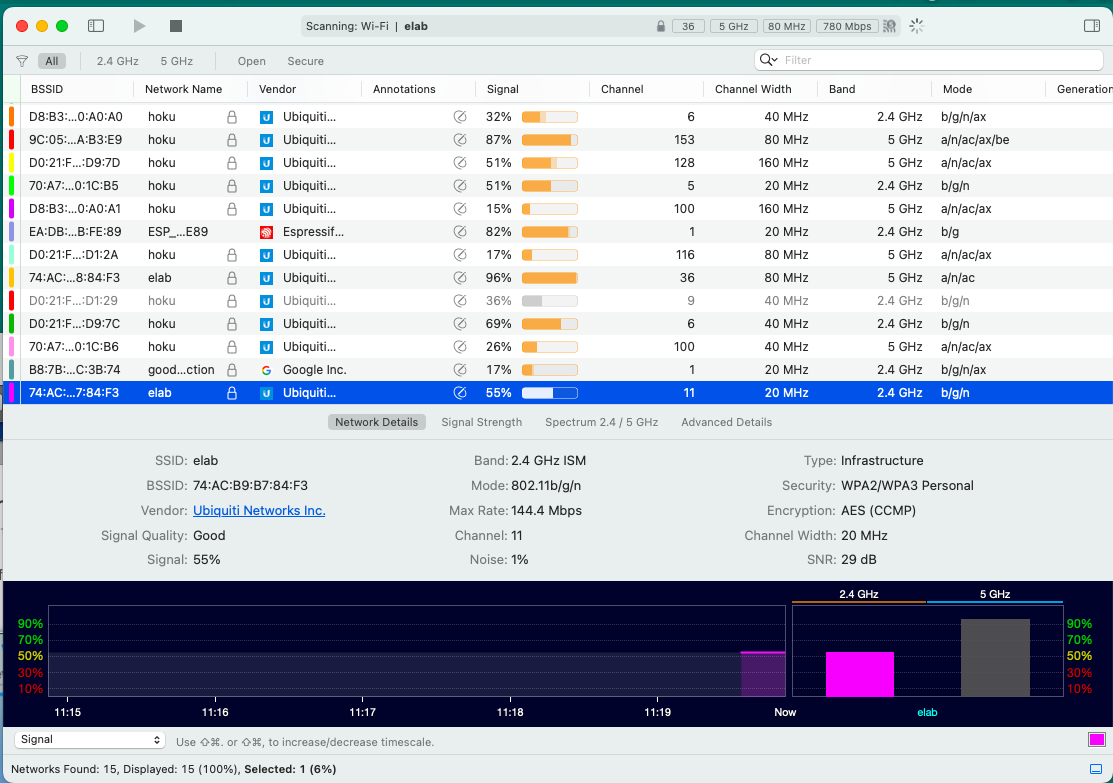Screen Shot 2025-09-10 at 11.19.53 AM.png
As a hacker, what do you have here that you don't have before? After setting up your own wifi, what do you see here that you can do to improve the security of yours?
How could you use this tool and the OUI lookup tool online to get into a network?
Is there a site that lists all of the default passwords for access points? Find it and lookup a few from your scans...
Try joining a wireless network then use some of the scanning tools you already know:
- IP net monitor
- network radar
- iNet scanner
- IP scanner
- network kit
Some technical details:
Wifi uses one of three radio bands:
- 2.4 gHz: long range, lower data rates, stopped by water, wet leaves, humans
- 5.8 gHz: shorter range, higher data rates, goes through water better
- 6 gHz: very short range, humongous data rates, no issues with water
Signal and noise:
Try talking with someone who is in the shower: you can hear them, they can't hear you-why?
Same signal (speech) but your noise level is lower (high signal to noise ratio).
Shower person has high noise, same signal, low signal to noise ratio.
This is crucial....
MIMO: multiple in, multiple out and other ways access points "steer" radio beams
If many people are on the same access point, the AP has to keep steering beams to everyone, overloading it.
If some users are at the limit of range (fringe users) this slows the entire network slows down: "can you hear me now?"
Setting up wifi networks:
- look at the spectrum diagram
- notice any overlaps
- change the channel on your AP so that it is not overlapping
- re-check your signal levels
Questions:
1. How will this enable you to improve the wifi at home?
2. What did you learn doing this that can improve your user experience?
3. How many "illegal" wireless networks did you find on campus?
4. Please email screenshots of what you find
Catching up:
- Make sure you have completed the cyber challenge #1
- Make sure you have completed the router setup challenge
If you are ready for a deeper dive into setting up wifi networks, pick one of the mikrotik devices and see if you can configure it for a wifi network and NAT to your inside machine
---
Migrated from Apple Server Wiki. Original page ID: 31L2K5g
# Module 5.2: Encryption and protocols
[Download Module 5 Pt 2.pdf (application/pdf, 435.2 KB)](https://bookstack.kamuela.org/attachments/325)
### Module 5: Cybersecurity Pt. 2
### Key Terms:
- Malware
- Types of malware
- C2 servers
- Examples
- Protocols
- Definition
- Common protocols
- DNS
- Cryptography
- Hashing
- Encryption
- Usages
- Malware
- Malware is a word most people know nowadays from tech stuff, movies, etc.
- Malware = Malicious Software
### Module 5: Cybersecurity Pt. 2 1
We’ve talked a bit about different types of hacking/pentesting in the first part of the module, so lets look at some real-life examples of malware used for hacking:
- Virus
- Malware that inserts itself into legitimate programs to look real
- Worm
- Self-replicating malware that spreads itself to as many computers as possible
- Trojan
- Malware that disguises itself as “real” software
- Ransomware
- Malware that encrypts user files/data and locks it until the user pays money
- Keylogger
- Malware that records what the user types and sends it back to the hacker
In all of these cases, the main purpose of malware is to gain access into networks so that the hackers can leverage authentication to steal money, data, info, etc
### Module 5: Cybersecurity Pt. 2 2
In the cybersecurity field, we don’t really use the word hacker ever, instead we call them threat actors.
What is a C2 server?
A Command and Control (C2) server is like the mission control center for any malware. It is where all the stolen data is sent to from malware once it is successfully put on a users computer/network.
How it works:
1\. A threat actor will put malware onto a persons computer successfully and compromise it
2\. The malware will try to connect back to the attacker’s C2 server (which is typically hidden)
3\. The C2 server will then send commands, receive stolen data, and remotely update/change the malware itself.
Common Protocols Used:
- HTTP/HTTPS (blends in with normal traffic)
- DNS (used for covert tunneling)
- IRC (older botnets)
- Custom encrypted protocols over TCP
### Module 5: Cybersecurity Pt. 2 3
Malware isn’t only used by individual people, but governments are also known for using malware to spy on each other and in some cases cause physical damage,
such as:
Stuxnet (2009-2010)
One of the most famous pieces of malware ever written of all time, designed by the United States government as a cyberweapon to sabotage Iran’s nuclear enrichment facilities.
The malware would slowly over time make their physical centrifuges run faster and faster until they actually broke down into pieces.
[https://en.wikipedia.org/wiki/Stuxnet](https://en.wikipedia.org/wiki/Stuxnet)
WannaCry (2017)
Ransomware that was spread globally to over 300,000 machines, demanding bitcoin from the users in order for their data to be decrypted
Caused a lot of money in damages and messing up computers all over the world
[https://en.wikipedia.org/wiki/WannaCry\_ransomware\_attack](https://en.wikipedia.org/wiki/WannaCry_ransomware_attack)
### Module 5: Cybersecurity Pt. 2.4
watch this video on stuxnet, insane stuff:
[https://www.youtube.com/watch?v=WyBlh8Tq6\_Q](https://www.youtube.com/watch?v=WyBlh8Tq6_Q)
Protocols
What are protocols?
Protocols are basically a set of rules of how computers talk to each other.
Every time you do something on a computer like opening a website, sending a text, or streaming a video, your computer is using multiple protocols to make sure that everything is sent, received, and understood properly.
Common Protocols:
TCP
- Used when accuracy matters (ex: loading a website or sending an email)
- Slower, but reliable — makes sure every packet is received
- HTTP example
### Module 5: Cybersecurity Pt. 2 5
- UDP
- Used when speed matters more than reliability (ex: video calls, games)
- Packets might get dropped or arrive out of order
- No handshake
- Used by websites to send data like HTML, images, and scripts
- Works on port 80
- Doesn’t encrypt anything — all data is sent in plain text
- ARP
- Used by your computer to determine the MAC address of devices locally before sending or receiving data
- Essentially helps your computer determine where to send packets/info
ICMP
- Used to send error messages, tests (such as pings), and status updates
- Helps determine and diagnose smaller problems
- This will be on the next quiz, so remember this example very specifically
- (essentially a free point if you’re reading the modules):
When you visit a website:
- HTTP sends the webpage
- ICMP says “This device is online” or “The page isn’t loading because the network isn’t responding”
Recap on stuff you learned earlier:
DNS (Domain Name System)
### Module 5: Cybersecurity Pt. 2 6
- DNS converts names like google.com into IP addresses like 142.250.190.78
- Happens every time you visit a site
Real Examples:
You connect to a website:
1\. DNS resolves domain
2\. TCP handshake starts
3\. HTTP or HTTPS request is sent
You join a game:
1\. UDP is used to send quick game state updates
Hashing, Cryptography, and Encryption
### Module 5: Cybersecurity Pt. 2 7
So what do we even do if there’s a million ways for viruses to steal our info?
When we talk about network security, we’re really just talking about protecting information and making sure it doesn’t get stolen, changed, or seen by anyone we don’t know.
Think of it like this:
Hashing = locking something in a box and throwing away the key
Encryption = locking something in a box with a key, so only the right person can open it
Hashing:
A hash takes any input and turns it into a long sequence of letters and numbers.
example:
"mypassword" → ef92b778bafe771e89245b89ecbc08a44a4e166c06659911881f
Why do we use it?
To store passwords safely
To check file integrity (if a file changes at all, the hash will completely change)
An example is SHA256, try it out:
[https://emn178.github.io/online-tools/sha256.html](https://emn178.github.io/online-tools/sha256.html)
type in your name or anything you want, then change just one letter and see what happens
### Module 5: Cybersecurity Pt. 2 8
Encryption:
Encryption takes an input and gives you the encrypted version along with a specific key to decrypt it.
Types of Encryption:
1\. Symmetric Encryption (One key)
a. The same key is used to encrypt and decrypt (lock and unlock)
b. Fast and easy to use
c. Since there is only one key, sharing the key with people has to be done
safely
2\. Asymmetric Encryption (Two keys)
a. You have a public key and a private key
b. Anyone can use your public key to lock a message for you
c. Only your private key can unlock it
Some examples of people/businesses that use encryption are:
- Messaging apps (WhatsApp, iMessage, Signal)
- Banking websites (Chase, Wells Fargo, etc)
- Cloud services (AWS, Azure, GCP)
If you’ve gotten to the end of this, make sure you know these for the upcoming quiz:
Malware and types of malware
### Module 5: Cybersecurity Pt. 2 9
- C2 servers
- Stuxnet
- HTTP and ICMP (look at the example I put above)
- Hashing and Encryption
Module 5: Cybersecurity Pt. 2 10
---
Migrated from Apple Server Wiki. Original page ID: D7s458n9
# Module 4.2: Rogue wifi challenge
1. Choose one of the Mikrotik routers in the lab, and using your iMac wired connection, configure a hidden wifi network and NAT to enable ssh into your iMac from the WAN.
2. Challenge your friends to login to your iMac by the WAN connection and create a folder there with a secret message (just like planting a virus)
3. Challenge your friends to find the wireless network that you have hidden based on the MAC address of the mikrotik device
4. Hide your mikrotik router somewhere in the elab connected to power (no WAN connection needed)
5. Challenge your friends to find the hidden access point.
---
Migrated from Apple Server Wiki. Original page ID: 727846f3J
# Module 4.3: Cyberchallenge #3: wireless networks
Please read this about wifi security and answer the following questions:
Take Control of Your Wi-Fi Security (1.7).pdf
[Download Take Control of Your Wi-Fi Security (1.7).pdf (application/pdf, 1.4 MB)](https://bookstack.kamuela.org/attachments/331)
Take Control of Your Wi-Fi Security (2.0)
[Download Take Control of Wi-Fi Networking and Security (2.0).pdf (application/pdf, 2.4 MB)](https://bookstack.kamuela.org/attachments/327)
questions:
1. Imagine you are setting up a wifi network for your own home. What are the three L’s for you here? (likelihood, liability, lost opportunity)
2. Now repeat for a doctor’s office: likelihood, liability, lost opportunity
3. Now repeat for an airline that has a website for making reservations
4. Why should you avoid using public wifi at airports and coffee shops?
5. Are there any data in your life that is sent in the clear?
6. What is the difference between data theft, data damage and sidejacking?
7. Are all zombie attacks malicious? Does the launching user always know they are attacking? How?
8. Why is making your network hidden a nice first step for casual users, but not really secure to hackers (like you)?
9. What are the three simple config changes to a router you can make?
10. Why are MAC address controls nice but not really secure?
11. If you setup guest access at your home wifi, what are guests able to do, and what are they not able to do?
12. Table 2 shows an increasing level of security-where do you fit in and why?
13. Why do some websites get blocked as “insecure” by some browsers, and what are the solutions?
14. When you used ssh to get into another computer, you had to say “yes” to enable this-why?
15. We watched passwords being sent over the network with FTP. How would this be different for SFTP?
16. You might be using a VPN to download stuff, or to view programs in another country. Are they really secure, or is this just something the company says to sell their VPN product?
17. Why would using NAT be better than using a DMZ host?
18. What are SPI and DPI?
19. How do you setup a firewall on your personal mac?
20. You might see WPA personal or WPA enterprise-what are these?
---
Migrated from Apple Server Wiki. Original page ID: B3N150T
# Module 5.1: Network security: pentesting, VPNs
## Subsections
- Kali
- Network Security
- Firewalls
- VPNs
- Wireshark
- Cryptography
- Malware
- Social Engineering
- The cloud
Key terms:
- Kali linux
- Pentesting
- Network security
- VPNs
- Firewalls
## Kali linux
What is Kali and why do people use it?
Kali Linux is a type of distribution of Linux that has a lot more tools for hacking/pentesting/info gathering. It comes installed with a bunch of tools such as:
- nmap
- whois
- netstat
- wireshark
imagine linux but fine-tuned for hacking
Remember wireshark and nmap, these two are really popular and used by people in the industry
some examples of using these tools (don’t do these, they aren’t legal):
I want to see all the traffic going through the network and what people are looking up
Kali → Wireshark → sniff for packets being sent on the network → decode the packets and gather info
I want to brute force my own password for testing purposes
Kali → John the Ripper → get a dictionary full of words → run a brute force attack that tests every possible combination of words and letters against the password
I want to see all the people that are connected to the same wifi as me
Kali → nmap → network scan → look at all connected devices and their IP addresses
people who work in the industry are hired use these tools often, such as:
- working for a company using these tools to monitor their security and see any potential threats
- hired by companies to test their security and try to find vulnerabilities which they then report back to the company
## Pentesting
What is pentesting?
Penesting (aka penetration testing) is using tools like the ones listed above to simulate real-life attacks on computers, networks, databases, etc.
Remember earlier when I said people who work in industry are hired for this?
People are paid lots (and I mean lots) of money to simulate hacking into companies, as a hired expert finding a vulnerability is cheaper for a company than actually getting attacked by a group of hackers. These are also known as bug bounties, essentially looking for bugs or vulnerabilities within a company, finding them, then reporting back to the company and getting paid.
[https://immunefi.com/bug-bounty/](https://immunefi.com/bug-bounty/)
What are some common methods of pentesting/hacking?
- OSINT (Open source intelligence)
- Looking for publicly available information about individuals to potentially find sensitive information as leverage to gain access to accounts or privileges.
- Dictionary attacks
- Using a list of common passwords to guess login credentials
- Brute force attacks
- Using every possible combination of characters until the correct one is found
- Phishing
- Sending fake emails, messages, etc to pretend to be someone else and gain sensitive data
- Man in the middle attacks (MITM)
- Intercepting online communication between two systems to gain information or steal data
- Social engineering
- Tricking people into giving sensitive info, similar to phishing but more human-based and less technical
## Network Security
What is a network?
A network is a connection of two or more devices that send information to each other
As you know from previous modules, IP addresses are used by computers to send information to each other and create a network
Network Security involves protecting the connections between devices so that third parties cannot steal data or get info illegally
Try running these commands on your computers:
Mac:
```
lsof -i -n -P | grep LISTEN
```
Windows:
```
netstat -ano | findstr LISTENING
```
this tells you open ports, processes going on, and other info about what your computer is actively doing
Some people use VPNs (virtual private networks) to create secure connections between their computer and other devices to conceal their real IP and identity
People also use Firewalls to protect their stuff, and your computer by default most likely has a basic firewall setup to prevent you from downloading and running malicious programs like viruses. Firewalls work by monitoring traffic on your computer and deciding what to allow or block.
Important to remember: Firewalls work by viewing packets, just like how wireshark is used to sniff packets being sent across the internet.
Firewalls exist for both hardware and software (both physical computers and applications) and are built into routers, pc parts, and common apps
Network security is of course much more complex than these short definitions, but it can all be boiled down to information being sent to and from computers, and how we protect that information.
## Wireshark
Wireshark is a tool that lets you view network traffic on both your computer and online networks.
the cool thing about a lot of these apps is that they’re open source, just like linux, and thus free to use and easy to understand how they’re built
lets try it out!
first, download wireshark from the website:
[https://www.wireshark.org/download.html](https://www.wireshark.org/download.html)
next, do these steps:
1. open wireshark
1. you’ll see a list of available network interfaces, such as wifi, ethernet, etc
1. choose a network interface (i.e. wifi) and start a capture
1. this will start capturing all the packets sent on the wifi in real time
1. visit a website online, such as [http://neverssl.com](http://neverssl.com/) (this link works well because it not encrypted)
1. filter the traffic
1. in the filter bar, type “http” or “ip.addr == YOUR\_IP”
1. you can find your own IP by typing this in terminal: “ipconfig getifaddr en0” or “ipconfig” for windows
1. this narrows the traffic down to just your device
1. look inside one of the packets
1. click on a packet (look for ones marked “GET”)
1. expand and see all the info from the packet
1. you can now see the website you visited, the size of the packet, the destination IP addresses, and more
once you’re done, just click the red stop button and it’ll stop
congrats, you just used wireshark for the first time :)
---
Migrated from Apple Server Wiki. Original page ID: y7S562
# Module 6.1: Passwords
Please read this reference:
[Download Take Control of Your Passwords (4.2).pdf (application/pdf, 1.5 MB)](https://bookstack.kamuela.org/attachments/328)
- Tools:
- Homebrew: enables linux commands on mac terminal
- Parrot OS: runs virtually under UTM, security suite
- Kali Linux: runs virtually under UTM, native on linux boxes
- Debian Linux: runs on raspberry pi as "raspian"
- Latest version of raspian is bookworm...
Apps, images and scripts can be found here: (the German server)
[https://10.14.4.91:3670/files/hpa/cybersecurity/](https://10.14.4.91:3670/files/hpa/cybersecurity/)
First install homebrew: [https://brew.sh](https://brew.sh)
/bin/bash -c "$(curl -fsSL [https://raw.githubusercontent.com/Homebrew/install/HEAD/install.sh](https://raw.githubusercontent.com/Homebrew/install/HEAD/install.sh))"Install these on your mac:
```
brew install pwgen brew install hashcat brew install john brew install openssl brew install cracklib brew tap jzaleski/homebrew-jzaleski brew install apg
```
single command:
```
brew install pwgen hashcat john openssl cracklib
```
Note:
- All of the files you create will be in the root directory of you, the admin user on your computer
- I'll use italic for all commands, and use ------ to separate commands from notes, don't include them in your scripts
How many passwords are out in the wild?
look at this password list:
[https://weakpass.com/wordlists/rockyou.txt](https://weakpass.com/wordlists/rockyou.txt)
What do you notice?
---
Migrated from Apple Server Wiki. Original page ID: F634j547
# Module 5.3: Wireshark challenge
Wireshark overall plan:
- learn how to read networks using nmap and ipnetmonitor
- install wireshark and learn how to read packets
- learn about the dialog all machines use on the internet (DNS, ARP, ACK-SYN, ICMP)
- learn how to install a wireless router to create an isolated hacker network (hackz0rz)
- use this network to attack and defend using metasploit
- learn how to protect yourself
Downloading parrot-os:
1. go to elab.hpa.edu
2. look for computer engineering lower folder (bottom of page)
3. look for installers folder
4. download UTM and parrot-os.utm images
5. install on your own laptop
6. go to wireshark.org and install the version that matches your computer (windows, mac, apple silicon)
7. open wireshark and begin your challenge
Wireshark challenge: Part 1: http
Your challenge is to view the login credentials of an insecure http request using wireshark
1. start wireshark
2. choose an active network interface (look for the squiggly lines)
3. apply the http filter
4. go to the IP address posted on the board
5. start packet capture
6. refresh the page
7. login to the admin pages (see board for credentials)
8. stop the packet capture
9. look through the packets for a POST entry
10. find the login and password you used
11. repeat this with another host
12. repeat using the http.request filter
Wireshark challenge: Part 2: arp and icmp
1. open terminal
2. run ping to another machine
3. start wireshark with the arp filter
4. repeat with the icmp filter
5. what is the MAC address of the sender and recipient?
6. what was the round trip time for each packet?
Wireshark challenge: Part 3: ACK-SYN
1. open a browser and visit a non-https host
2. filter with tcp in wireshark
3. fine a tcp 3-way handshake
4. what does ARP do, and why did it appear before the ping?
5. what do ICMP messages tell us about connectivity?
6. how can this delay help identify potential network intrusions?
Server challenge:
1. setup an apache server on one of the raspberry pi units
2. password protect some part of the web server (look up how to do this, either .htaccess or another method)
3. share your IP address with another student (the "attacker")
4. have them watch using wireshark as you login
5. challenge them to gain your password
6. question: why do we gather packets for later use using pcap?
---
Migrated from Apple Server Wiki. Original page ID: E3H2f941
# Module 7.0: Digital privacy
[Text](https://elab.hpa.edu/cyber/Take%20Control%20of%20Your%20Passwords%20(4.2).pdf)
Topics:
- evolving landscape
- risks
- privacy strategy
- mail practices
- social media
- network privacy
- web privacy
- email
- chat
- mobile
- Iot
---
Migrated from Apple Server Wiki. Original page ID: g4h2k2X
# Module 6.2: Password checks
Using the terminal or parrot OS:
PW check: works on newer versions of homebrew and pi
- brew install cracklib (if not already installed)
- cracklib-check <enter password to check>
- try with several passwords
- optional format: echo "password123" \| cracklib-checkpassword generator:
- pwgen -sy 16 5
- generates 5 strong random 16-character passwords with symbols
- generate a few passwords with thisinstall apg: auto pw generator
- brew tap jzaleski/homebrew-jzaleski
- brew install apg
- generate a few passwords with this
try it out:
- apg -m 12 -x 16 -n 5
- 5 passwords between 12 and 16 characters.
Try each of these with cracklib-check at least three times
---
Migrated from Apple Server Wiki. Original page ID: s2y1u3T8
# Module 6.4: Password hashing
Hashing:
A hash takes any input and turns it into a long sequence of letters and numbers.
Example:
- "mypassword" → ef92b778bafe771e89245b89ecbc08a44a4e166c06659911881f
- Why do we use it?
- To store passwords safely
- To check file integrity (if a file changes at all, the hash will completely change)
An example is SHA256, try it out:
[https://emn178.github.io/online-tools/sha256.html](https://emn178.github.io/online-tools/sha256.html)
type in your name or anything you want, then change just one letter and see what happensI made one for testing:
da355c585ad36b98017d11ed3fd05199acbb2855345dc463f61fc42fdf6656c9
is a SHA256 hash of Toomanysecrets77
Challenge:
1. repeat the hash with the same password using different encodings: MD5, SHA256, SHA512
2. what do you notice?
Encryption:
Encryption takes an input and gives you the encrypted version along with a specific key to decrypt it.
Types of Encryption:1. Symmetric Encryption (One key)
a. The same key is used to encrypt and decrypt (lock and unlock)
b. Fast and easy to use
c. Since there is only one key, sharing the key with people has to be done
safely
2. Asymmetric Encryption (Two keys)
a. You have a public key and a private key
b. Anyone can use your public key to lock a message for you
c. Only your private key can unlock it
Some examples of people/businesses that use encryption are:
- Messaging apps (WhatsApp, iMessage, Signal)
- Banking websites (Chase, Wells Fargo, etc)
- Cloud services (AWS, Azure, GCP)
Tools:
- Hashing app: [https://emn178.github.io/online-tools/sha256.html](https://emn178.github.io/online-tools/sha256.html)
- Hashcat: [https://www.youtube.com/watch?v=mo\_vh0BCA\_g](https://www.youtube.com/watch?v=mo_vh0BCA_g)
- Kali video: [https://www.youtube.com/watch?v=z4\_oqTZJqCo](https://www.youtube.com/watch?v=z4_oqTZJqCo)
---
Migrated from Apple Server Wiki. Original page ID: W0N6N6
# Module 6.3: Password integrity-entropy
- Entropy is a measure of disorder.
- In our case, high entropy is good, as it makes it harder for hackers to guess your password.
- OSINT (open source intelligence) is a different matter-these are based on human things like pet names, birthdays, etc.
How good are your passwords?Create a password entropy checker:In your terminal, enter the following:
```
sudo nano entropy_calc.py
```
paste the text below into the window, then ctrl-o and ctrl-x:
\--------------
```
# entropy_calc.py import math,sys def entropy(password): L = len(password) N = 0 if any(c.islower() for c in password): N += 26 if any(c.isupper() for c in password): N += 26 if any(c.isdigit() for c in password): N += 10 if any(not c.isalnum() for c in password): N += 33 # rough symbol set return 0.0 if N==0 else L * math.log2(N) pw = sys.argv[1] print(f"{pw}: length={len(pw)} entropy≈{entropy(pw):.1f} bits")
```
---------------How to use:
```
python3 entropy_calc.py 'Password123' python3 entropy_calc.py 'correcthorsebatterystaple'
```
Look at the results
Try with the passwords you generated beforecreate a password checker program:
```
sudo nano zxcvbn_demo.py
```
paste this into the window, then ctrl-o and ctrl-x:
\-----------------
```
#!/usr/bin/env python3 # zxcvbn_demo.py # Usage: python3 zxcvbn_demo.py password1 "another password" # Or: echo -e "pw1\npw2" | python3 zxcvbn_demo.py import sys try: from zxcvbn import zxcvbn except Exception as e: print("Error importing zxcvbn. Install via: pip3 install zxcvbn(or `npm i -g zxcvbn` and use node fallback).") raise def analyze(pw): r = zxcvbn(pw) print("="*60) print("Password:", pw) print(" score (0-4):", r.get("score")) print(" guesses (est):", r.get("guesses")) print(" guesses_log10:", r.get("guesses_log10")) fb = r.get("feedback") or {} if fb.get("warning"): print(" warning:", fb.get("warning")) if fb.get("suggestions"): print(" suggestions:") for s in fb.get("suggestions"): print(" -", s) # show match breakdown (if present) matches = r.get("sequence", []) if matches: print(" pattern matches (top few):") for m in matches[:5]: print("-", m.get("pattern"), m.get("token"), f"(i:{m.get('i')}, j:{m.get('j')})") print() def main(): inputs = [] if not sys.stdin.isatty(): inputs += [l.strip() for l in sys.stdin if l.strip()] if len(sys.argv) > 1: inputs += sys.argv[1:] if not inputs: print("Usage: echo 'pass1\npass2' | python3 zxcvbn_demo.pyOR python3 zxcvbn_demo.py pass1 pass2") sys.exit(1) for pw in inputs: analyze(pw) if __name__ == "__main__": main()
```
-----------------------Try it out:
```
python3 zxcvbn_demo.py Password123 "correct horse battery staple"
```
or
```
echo -e "Password123\nTr0ub4dor&3\ncorrecthorsebatterystaple" | python3 zxcvbn_demo.py
```
```
scripts to use: download the file below
```
```
```
```
unzip sudo chmod +x setup_commands.sh ./setup_commands.sh python3 entropy_demo.py
```
```
```
[Download raspi\_cyber\_labs.zip (application/zip, 5.8 KB)](https://bookstack.kamuela.org/attachments/332)
---
Migrated from Apple Server Wiki. Original page ID: S9X8T7
# Module 6.5: Brute force attacks: Hydra
Brute force dictionary attacks: hashing, hashcat and hydra
Install hydra and hashcat: home brew example
```
brew install hydra hashcat
```
On linux machines:
```
sudo apt install hydra hashcat -y
```
```
Hashcat:
```
```
```
- decodes hashes by comparing them with a wordlist of known hashes
- you must have a local copy of the hashes to do this
- if you have a modern gaming GPU, this can be very fast
- you don't have to maintain a connection to do this once you have the hashed file
- can use huge dictionary to decode hash
```
Hydra:
```
```
```
- does the same using ssh to attack a remote computer
- must have a constant connection to the computer to attack (e.g. can be detected)
- can attack computers inside a network, but not through firewalls
- can make millions of attacks per second using a large dictionary stored locally
>
Hashing:
```
```
Example:use the online utility to create a SHA512 hash for Toomanysecrets77:
da355c585ad36b98017d11ed3fd05199acbb2855345dc463f61fc42fdf6656c9
is a SHA256 hash of Toomanysecrets77 (a secret password)
try this out, make sure you get the same resultLocal password attack demo: hashcat
create your own word list of passwords:
```
sudo nano wordlist.txt
```
insert these, one on each line:
```
papaya77 Toomanysecrets77 hashcat pal82
```
ctrl-o, save and then ctrl-x
next: create another file on your machine:
```
sudo nano hashes.txt
```
Generate SHA512 hashes for each password and copy the hashes into this file, ctrl-o, save, ctrl-x
Run hashcat to decode the hashes:
**hashcat -m 1400 -a 0 hashes.txt wordlist.txt
or this
**sudo hashcat -m 1400 -a 0 hashes.txt wordlist.txt --outfile=cracked.txt --outfile-format=2
show results:
**sudo hashcat --show -m 1400 hashes.txt**
what does this do?
1. opens hashcat
2. decodes format 1400 (SHA512 encryption) (mode)
3. attack mode, dictionary attack (-a)
4. use these two files
what do you see?
try again using this password file:
[Download common-passwords.txt.zip (text/plain, 2.2 KB)](https://bookstack.kamuela.org/attachments/336)
[Download crackedpasswords.txt (text/plain, 82 B)](https://bookstack.kamuela.org/attachments/337)
You will have to change the 1800 encryption code to another number
what is the hidden password?
Remote dictionary attack: using hydra
sudo hydra -l "pi" -P wordlist.txt \\
10.14.88.83 ssh
enter the password for YOUR machine to connect by ssh
This is an external attack...
1 of 1 target completed, 0 valid password found
What did you find?Why does it fail?Salting: adding random characters to confuse hashcat
ssh into the machine at 10.14.88.83 (pi/papaya77)
```
cd /etc cat shadow
```
find the hashed entry for the user pi
$y$j9T$bl0cC/JggW3QeHa3UyiNc0$23oSBAPMIvOng71RwU4qZGLChAcwWCjJYm/jAaHavOB
This is a salted hash, meaning random characters have been inserted between the hash to make it more secure.
Massive wordlists:
Download this massive list of passwords:
[https://weakpass.com/wordlists/rockyou.txt](https://weakpass.com/wordlists/rockyou.txt)
expand the file:
```
sudo gzip -d rockyou.txt.gz
```
Look at the file:
```
cat rockyou.txt
```
crazy!
---
Migrated from Apple Server Wiki. Original page ID: 64m6w3W5k7
# Module 6.0: Password labs
1. download the TCO book about passwords to your own mac so you can complete the homework
2. install homebrew on your mac: module 6.1
3. follow the instructions in module 6.1 to install the brew commands on your laptop
4. test these out by typing brew update and pwgen-you should see a password generator
5. in class, we will be using older pimacs as well as your personal macs, once you have installed homebrew
Password quality checks: 6.2
1. start with cracklib-check (see module 6.2)
2. move on to pwgen and apg
3. create at least 5 passwords and record them from each, we'll use them next
Entropy: 6.3
1. follow the steps on module 6.4 to create the python script entropy\_calc.py
2. test the program by: python3 entropy\_calc.py
3. using the password checker program entropy\_cal.py check each of your 5 passwords
4. repeat with simpler passwords
5. repeat with the zxcvbn\_demo.py script or the entropy\_demo.py script if you have it
6. from the homework, why do we care about entropy?
Hashing: 6.5
1. try out hashing using this site: [https://emn178.github.io/online-tools/sha256.html](https://emn178.github.io/online-tools/sha256.html)
2. create hashes from your 5 passwords above
3. hide these in a file called hashes.txt
4. challenge your friends to find that file for later
5. follow the tips on module 6.5 to install hashcat if not installed already
6. follow 6.5 to create a small wordlist with your original 5 passwords along with papaya77
7. follow 6.5 to run hashcat and decode the hashes
8. if you had a much bigger wordlist, would you be able to attack a new machine?f
9. follow 6.5 to use hydra to attack 10.14.88.83
10. explain why the hash could not be decoded
---
Migrated from Apple Server Wiki. Original page ID: h2U3\_495
# Module 7.1: Evolving landscape: how secure are you online?
Internet security audit:
1. look up the breaches on page 15
2. search online for your name in the breaches if you can (google etc.)
3. go to my account on google and opt out of data collection
4. if you use venmo, check if your transactions are private
5. check yourself on [https://haveibeenpwned.com/](https://haveibeenpwned.com/)
6. check all of your email addresses-is the information correct?
7. look yourself up on a data broker
8. go to [https://amiunique.org ](https://bookstack.kamuela.org); what is shown?
9. save a screenshot of what is shown
10. open a private or incognito window and repeat
11. compare the uniqueness score what what changed
12. go to [https://coveryourtracks.eff.org](https://coveryourtracks.eff.org)
13. try [https://privacy.net/analyzer/](https://privacy.net/analyzer/)
14. try this site with various websites: [https://themarkup.org/blacklight](https://themarkup.org/blacklight)
15. try with hpa.edu
16. repeat with this checker: [https://webbkoll.dataskydd.net/en/](https://webbkoll.dataskydd.net/en/)
17. insecure camera list: [http://www.insecam.org/](http://www.insecam.org/)
18. go here and search for SCADA [https://www.shodan.io/](https://www.shodan.io/)
19. Have you been sold? [https://haveibeensold.app](https://haveibeensold.app/)
20. why is HPA so serious about your photo and name on web pages?
21. how does facial recognition change this?
22. check out this listing: [https://privacyrights.org/data-breaches](https://privacyrights.org/data-breaches)
23. and this one: [https://en.wikipedia.org/wiki/2010s\_global\_surveillance\_disclosures](https://en.wikipedia.org/wiki/2010s_global_surveillance_disclosures)
---
Migrated from Apple Server Wiki. Original page ID: B5y7J0A4
# Module 7.2: Your risk profile
- try changing your DNS server from 8.8.8.8 to something else-why?
- use IP net monitor, TCPdump or wireshark to monitor your web traffic while browsing with chrome
- do the same as you go to google docs or google drive-what do you see?
- watch traffic while we have the elab web blocker active, then without
- if you are interested, create your own adblocker with pihole, a blocking server
- list at least three VPN providers you can use-are these totally secure?
- follow the instructions on page 53 to delete info google has stored on you:
1\. Go to the Data & privacy portion of your Google Account page and
sign in if you’re not already signed in.
2\. Scroll down to “Things you’ve done and places you’ve been.”
3\. Under “History settings,” click Web & App Activity.
4\. Click “Turn off.”
5\. Click Pause.
6\. When the “Setting is off” window appears, click “Delete old activity.”
7\. Click “All time.”
8\. Click Delete.
9\. Now repeat steps 4–8 with Timeline and YouTube History.
10\. Under “Personalized ads,” click My Ad Center.
11\. Click the On button in the top-right corner of the window, and
then click “Turn off.” Confirm by clicking “Got it.”
- go to badbool and remove yourself from data brokers: [https://github.com/yaelwrites/Big-Ass-Data-Broker-Opt-Out-List](https://github.com/yaelwrites/Big-Ass-Data-Broker-Opt-Out-List)
- check out the other links on page 56
```
```
---
Migrated from Apple Server Wiki. Original page ID: i1K839
# Module 6.6: Parrot OS: passwords and insecure web
Parrot OS clean version:Parrot install:
sudo apt install pwgen hashcat john openssl apg libcrack2 passwdqc
Parrot OS already has most of thesecracklib-check is hidden:
/usr/sbin/cracklib-check
1. use /usr/sbin/cracklib-check to check several passwords
2. use pwgen to create 5 passwords, record these for later use
3. use apg to create 5 more passwords, record these as well
4. experiment with the generation format: apg -m 12 -x 16 -n 5 means 5 passwords between 12 and 16 characters.
5. try all of your passwords with cracklib-check (above)
6. go here: [https://emn178.github.io/online-tools/sha256.html](https://emn178.github.io/online-tools/sha256.html) and generate SHA256 hashes for your 10 passwords
7. create a password entropy checker (see code below)
8. evaluate the entropy of your 10 passwords
9. create a wordlist.txt file with the 10 passwords above, along with pal82 and papaya77
10. create a hashes.txt file with the 10 hashes from above
11. use hashcat to decode the hashes: hashcat -m 1400 -a 0 hashes.txt wordlist.txt
12. show your results: sudo hashcat --show -m 1400 hashes.txt
13. ssh into 10.14.88.83 and recover the hash for the pi user
14. attempt to decode this with hashcat
15. try a remote ssh password attack using hydra
16. use the command ip addr show to find your IP address
17. run python3 -m http.server 8000 to create a local web server
18. verify the local server is running at [http://127.0.0.1:8000](http://127.0.0.1:8000)
19. go to the IP address :8000 to verify the web server is running
20. browse the page while watching the terminal
21. use tcpdump to monitor packets locally
22. capture packets for analysis using wireshark
• 23. use wireshark to analyze the pcap file
---
Migrated from Apple Server Wiki. Original page ID: Q4V7L1k
# Reference: cybersecurity terms
Cybersecurity terms, principles, and history[https://cybersecurityguide.org/resources/cybersecurity-101/](https://cybersecurityguide.org/resources/cybersecurity-101/)Basic terminology
- To understand the vast world of cybersecurity or any technical field for that matter, the learner must master the words and phrases unique to that specialty.
- These terms and expressions will often have a related, but not entirely accurate meaning in general non-technical use.
- Without a clear understanding of how security professionals use certain words and phrases, learning about this specialty can be very confusing.
- Many words routinely used in security have such obscure origins that it is difficult to use them correctly without an understanding of their history.
As an example, the term pwn, or pwned, is commonly used by hackers. To understand how threat actors use pwn, it is helpful to know that this word likely comes from a common mistyping of “own” as a result of the proximity of the letter P to the letter O on a keyboard.
So if a hacker claims to have pwned a person or organization, they are laying claim to owning or conquering them.
The following definitions explain some of the terms, abbreviations, and acronyms commonly used in the security field.
- Attack surface: The attack surface of a software-based system is the sum of the different locations (logical or physical) where a threat actor can try to enter or extract data. Reducing the attack surface as small as possible is a primary security measure.
How does this compare to our analogy of a burglar invading a house?
- AV: Antivirus is a type of security software that scans for, detects, blocks, and eliminates malware. AV programs will run in the background, scanning for known malware signatures and behavior patterns that may indicate the presence of malware.
How is AI changing this?
- Brute-force attack: A brute-force attack is an attempt to decipher a username-password combination by trial and error. It is performed with software designed to try large samples of known username-password combinations. This method is an old attack method, but it’s still useful and popular with hackers.
How does this relate to our password lab? What are the 3 main mistakes people make about their passwords?
- Cryptoworm: A form of malware that spreads like a worm and encrypts victims’ data.
How is this different from a spearphishing attack?
- Data breach: A data breach refers to a security event where unauthorized users steal sensitive information from an organization’s IT systems. Often, stolen data is personally identifiable information (PII) or financial information, both of which are valuable on the dark web.
Refer to the three L's: which of these is relevant?
- EDR: Endpoint detection and response is a type of security tool that focuses on detecting and mitigating suspicious activity on devices and hosts. The value of EDR is the ability to detect advanced threats that may not have a recorded behavioral pattern or malware signature.
Look this up: compare centralized EDR to local EDR
- Firewall: A firewall is a network security system that monitors and controls the network traffic based on specific security rules. A firewall usually establishes a barrier between a trusted internal network and an untrusted external network, such as the Internet.
Compare your local firewall to the one you created with the routers-what is similar or different?
- Honeypot: A honeypot is a piece of software code designed to detect, deflect, and counteract attempts at unauthorized use of information systems. A honeypot consists of data appearing to be a legitimate part of the site but is isolated and monitored. The data seems to contain information, or a resource of value, to attackers, who are then blocked.
Look up "The cuckoo's egg" and explain how that worked
- IPS: An intrusion prevention system (IPS) is a form of network security that works to detect and prevent identified threats. Intrusion prevention systems continuously monitor a network, looking for possible malicious incidents, then capturing and reporting information about them.
Do we have one of these at HPA? At the elab?
- Malware: Malware is malicious software that propagates via an email attachment or a link to a malicious website. It infects the endpoints when a user opens the attachment or clicks on the link.
Compare static malware to dynamic malware
- NIST: The [National Institute of Standards and Technology (NIST)](https://cybersecurityguide.org/resources/nist-small-business-community/) is a non-regulatory entity under the umbrella of the United States Department of Commerce. NIST Publication Series 800 provides a comprehensive listing of information security measures and controls based on extensive research.
NIST also provides time synchronized sites for SSL-why would your computer not be able to access websites if the clock is wrong?
- Phishing/Spearphishing: A malicious email that tricks users into surrendering their user credentials. The email may appear legitimate as if coming from a bank and ask the user to reset their password. Phishing attacks take advantage of mass email programs. In a spearphishing attack, an individually crafted email targets a specific key executive or decision-maker.
Who is most likely to be vulnerable to these, and how can we protect organizations? Give an example at HPA.
- Ransomware: Ransomware is a class of malicious software that prevents the end-user from accessing a system or data. The most common form is crypto-ransomware. This type of ransomware makes data or files unreadable through encryption and requires a decryption key to restore access. Another form, locker ransomware, locks access rather than encrypting data. Attackers typically request a payment, often in the form of bitcoins, to decrypt files or restore access.
Again, come back to the three L's: who is most likely to be a victim and why?
- Ransomware attack: During a ransomware campaign, hackers often use phishing and social engineering to get a computer user to click on an attachment or a link to a malicious website. Some types of ransomware attacks, however, don’t require user action because they exploit site or computer vulnerabilities to deliver the payload. Once a system is infected, the attacker will launch an on-screen notification with the ransom demand.
Why are autonomous attacks (no user action needed) harder to prevent?
- Risk management framework: A Risk Management Framework provides a disciplined and structured process that integrates information security and risk management tasks into the system development life cycle. Essential components of an RMF include identification, measurement and assessment, mitigation, reporting and monitoring, and governance.
Why would companies NOT report attacks?
- Security misconfigurations: Security misconfigurations result from the improper implementation of security controls on devices, networks, cloud applications, firewalls, and other systems. They can lead to data breaches, unauthorized access, and other security incidents. Misconfigurations can include anything from default admin credentials, open ports, and unpatched software, to unused web pages and unprotected files.
Where have you seen this with the routers you setup?
- SOC: A security operations center (SOC) is a central location where cybersecurity personnel carry out threat detection and incident response processes. They employ security technologies that make up an organization’s security operations.
You are running a small office-can you afford to have an SOC? What are your options?
- SQL injection: An SQL injection is a technique that inserts structured query language (SQL) code into a web application database. Web applications use SQL to communicate with their databases. Attackers can use SQL injections to perform actions such as retrieving or manipulating database data, spoofing user identity, and executing remote commands.
Make a diagram of a website: "front end", "back end", data stream, and explain how an SQL injection attack works
- Tor: Tor is free and open-source software used to enable anonymous communication. Its name is derived from an acronym for the original software project name, “The Onion Router” and is sometimes referred to as such. Tor directs Internet traffic through a free, worldwide, overlay network consisting of more than seven thousand relays. It conceals a user’s location and usage from anyone conducting network surveillance or traffic analysis.
How is TOR different from a VPN?
- VA: Vulnerability assessment is the process of identifying, classifying, and prioritizing vulnerabilities in digital business systems. Assessments can focus on internal, external, or host-based vulnerabilities.
Could you make money doing one of these for a company or office?
•VM: Vulnerability management solutions identify, track, and prioritize internal and external cybersecurity vulnerabilities. They optimize cyberattack prevention activities such as patching, upgrades, and configuration fixes.
Who does this at HPA? At your house?
---
Migrated from Apple Server Wiki. Original page ID: 31h2v00
# Reference: cyber history
A brief history of cybersecurity[https://cybersecurityguide.org/resources/cybersecurity-101/](https://cybersecurityguide.org/resources/cybersecurity-101/)The 1970s
Cyber attacks span back through history to the 1970s. In 1971, Digital Equipment Corporation’s [DEC PDP-10](https://en.wikipedia.org/wiki/PDP-10) mainframe computers working on the TENEX operating system started displaying the message, “I’m the creeper, catch me if you can!” Dubbed [Creeper](https://www.techopedia.com/definition/24180/creeper-virus), this worm spread using the [ARPANET](https://www.britannica.com/topic/ARPANET), a forerunner to the Internet. It was created by Bob Thomas and was designed only to see if the concept was possible. Creeper laid the groundwork for viruses to come.
In response to the Creeper virus, Ray Tomlinson created Reaper. Reaper was the first antivirus software and was designed to move across the ARPANET and delete the self-replicating Creeper worm.
The 1980s
In September of 1983, the first cybersecurity patent was granted. Massachusetts Institute of Technology (MIT) was awarded this patent for a “[cryptographic communications system and method](https://patents.google.com/patent/US4405829A/en).” It introduced the [Rivest-Shamir-Adleman (RSA) algorithm](https://www.techtarget.com/searchsecurity/definition/RSA). RSA is one of the first public-key cryptosystems and is widely used for secure data transmission.
In 1986 the [Computer Fraud and Abuse Act (CFAA)](https://www.wired.com/2014/11/hacker-lexicon-computer-fraud-abuse-act/) was enacted to address hacking. It has been amended several times over the years to cover a broad range of conduct. The CFAA prohibits intentionally accessing a computer without prior authorization but fails to define what that means.
Also in 1986, Lawrence Berkeley National Laboratory systems manager [Clifford Stoll](https://en.wikipedia.org/wiki/Clifford_Stoll) learned that someone was hacking into the lab’s computer system. This discovery was made when Stoll tried to correct a 75-cent accounting error. Using a honeypot, Stoll determined that the lead hacker is [Markus Hess](https://peoplepill.com/i/markus-hess-1/), who had been selling information exfiltrated from hacked computers to the KGB. Hess and his accomplices were arrested by German authorities and convicted of selling stolen data to the Soviet Union. They only received suspended jail sentences.
In 1988 a Cornell University graduate student named Robert Morris released several dozen lines of code, which replicated wildly and spread to thousands of computers worldwide. The [Morris Worm](https://www.fbi.gov/news/stories/morris-worm-30-years-since-first-major-attack-on-internet-110218) crashed about 10 percent of the 60,000 computers then linked to the Internet. Morris became the first person convicted by a jury under the CFAA.
The 1990s
Cybersecurity systems, as we think of them today, really started to become popular in the early 1990s. Antivirus (AV) software was the first mass-produced cyber protection application on the cyber landscape. They appeared in the late 1980s, but the masses did not convert to the idea that they were necessary for several years.
These first antivirus systems, initially called [AV scanners](https://en.wikipedia.org/wiki/Antivirus_software#1980%E2%80%931990_period_(early_days)), were simple in functionality. They essentially scanned all the compiled code on a given system. They tested them against a database of known malicious signatures. The thinking was that as new viruses were discovered, these databases would be updated to watch for the new malware.
Researchers soon found out, however, that staying ahead of the bad guys was no easy task. The number of malware samples to check against grew from tens of thousands in the early 90s to millions of new samples each year, twenty years later. It is estimated that by 2014, as many as 500,000 unique malware samples were being produced every day.
These early software applications were resource-intensive and tended to bog down their host system. They also frustrated users with too many false-positive results.
[Secure Sockets Layer (SSL)](https://www.digicert.com/what-is-an-ssl-certificate) internet protocol is the security protocol that allows people to do simple things like purchase items online securely. Netscape released SSL 1.0 in 1994. After improvements, SSL became the core of the language for safely using the web, known as the Hypertext Transfer Protocol (HTTP).
In 1999,[ Kevin Mitnick](https://en.wikipedia.org/wiki/Kevin_Mitnick) pleaded guilty to four counts of wire fraud, two counts of computer fraud, and one count of illegally intercepting a wire communication. As the self-proclaimed world’s most famous hacker, he was sentenced to 46 months in prison plus 22 months for violating the terms of his supervised release sentence for computer fraud.
In his 2002 book entitled The Art of Deception, Mitnick asserts that he compromised computers only by using user names and passwords that he gained by social engineering. He maintains he did not use software programs or hacking tools for cracking passwords or otherwise exploiting computer or phone security.
In 1998, [Microsoft Windows 98](https://www.computerhope.com/jargon/w/win98.htm) was released, and this ushered in a whole new level of accessibility for the novice computer user. This increase in computer usage paved the way for software security systems to become common. Many new releases, updates, and patches soon followed. Security vendors discovered the vast market for security products intended for home users.
The 2000s
In 2003, the first universally known hacker group, [Anonymous](https://en.wikipedia.org/wiki/Anonymous_%28group%29), emerged on the scene. This group can be defined as a decentralized online community acting anonymously in a semi-coordinated manner, usually toward loosely self-agreed goals.
Over the years, dozens of people have been arrested for involvement in Anonymous cyberattacks around the world. Support of the group’s actions and effectiveness varies widely. Advocates have called the group freedom fighters and digital Robin Hoods.
In contrast, critics have described them as a cyber lynch mob or cyber terrorists. In 2012, Time Magazine called Anonymous one of the 100 most influential people in the world.
In recent years, however, Anonymous’s media exposure has declined, and they have largely vanished from the popular culture’s lexicon.
The late 2000s brought a whole new level of cyberattacks. Bad actors had developed an appetite for stolen credit cards. The years 2005 to 2007 were plagued by an ever-increasing frequency of data breaches.
To stem the flow of stolen data, governments around the world began to implement regulatory solutions. In the US, regulations required that authorities be notified when a breach was discovered and that funds be set aside to compensate victims.
The 2010s
The increased regulation of the 2000s proved to be too little, too late. The sophistication of hackers spiked as the profits seemed limitless.
Even nation-sanctioned bad actors with access to enormous funding could be observed battling for cyber-turf and waring over such prizes as online betting or gaming sites.
This decade saw the appearance and rise of [Endpoint Protection and Response systems (EPR)](https://www.digitalguardian.com/blog/what-endpoint-detection-and-response-definition-endpoint-detection-response). The systems replaced the legacy AV systems by including the same basic functionality but are radically improved and enhanced.
Instead of relying on a static signature to identify viruses, EPR scan for malware families. Malware samples follow a progression or mutation and so they can effectively be recognized as belonging to certain families even when no known malware signatures are detected.
Notable cybersecurity attacks
Each year brings with it a new spate of cyberattacks. Some reported by the victims in compliance with ever-stiffening government regulations and some uncovered by [Security analysts](https://cybersecurityguide.org/careers/security-specialist/). Largely because of their news value, the size of reported high-profile attacks is undoubtedly trending upward.
Some attacks catch the publics’ attention because of the name recognition of the victim. In contrast, others swindle large segments of the general population. Below are a few of the more notable cyberattacks over the last decade-plus.
[Learn more about cyber phishing attacks](https://cybersecurityguide.org/resources/phishing/)
Adobe
Adobe released information in October 2013 about the [massive hacking of its IT infrastructure](https://krebsonsecurity.com/2013/10/). Personal information of 2.9 million accounts was stolen.
Exfiltrated information included logins, passwords, names, and credit card numbers with expiration dates.
Another file discovered on the Internet later brought the number of accounts affected by the attack to 150 million. To access this information, the hackers took advantage of a security breach related to security practices around passwords.
Adult Friend Finder
In 2015, this dating site was attacked for the first time.
The information revealed included pseudonyms, dates of birth, postal codes, IP addresses, and sexual preferences of 4 million accounts.
This stolen data was made public on a forum only accessible on Tor. Malicious actors obtained these files; however, no banking data had been hijacked.
The following year, [Adult Friend Finder](https://www.zdnet.com/article/adultfriendfinder-network-hack-exposes-secrets-of-412-million-users/) faced a new attack, even more severe than the first one. This time more than 400 million files were exposed.
The stolen information was less sensitive, but in total, 20 years of personal information were taken.
Alteryx
This marketing analytics firm left an unsecured database online that [publicly exposed sensitive information for about 123 million U.S. households](https://www.forbes.com/sites/thomasbrewster/2017/12/19/120m-american-households-exposed-in-massive-consumerview-database-leak/#31c801627961).
The information included 248 fields of data for each home, ranging from addresses and income to ethnicity and personal interests.
Details included contact information, mortgage ownership, financial histories, and whether a household contained a pet enthusiast. Names were not included.
Equifax
Equifax, an American credit company, revealed, six weeks after the fact, that it had [suffered a cyberattack](https://www.csoonline.com/article/567833/equifax-data-breach-faq-what-happened-who-was-affected-what-was-the-impact.html) over the course of several months.
Detected in July of 2017, it contained personal data such as names, birthdates, social security numbers, and driver’s license numbers.
It also exposed 200,000 credit card numbers. Victims included 143 million American, Canadian, and British customers.
ILOVEYOU Virus
[ILOVEYOU](https://computer.howstuffworks.com/worst-computer-viruses.htm#pt2), sometimes referred to as Love Bug or Love Letter for you, is a computer worm that infected over ten million personal computers on and after May 2000.
It started circulating as an email message with the subject line “ILOVEYOU” and the attachment “LOVE-LETTER-FOR-YOU.
Marriott
Personally identifiable[ information from up to 500 million guests at the Marriott-owned Starwood hotel group](https://www.nytimes.com/2018/11/30/business/marriott-data-breach.html) was compromised, beginning in 2014.
The rift was first detected in September 2018.
Data exfiltrated includes payment information, names, mailing addresses, phone numbers, email addresses, passport numbers, and even details about the Starwood Preferred Guest (SPG) account.
NotPeta Malware
Petya is a class of encrypting ransomware that was first discovered in 2016. The malware targets Microsoft Windows-based systems.
It infects the master boot record and executes a payload that encrypts a hard drive’s file system table and prevents Windows from booting. It subsequently demands that the user make a payment in Bitcoin to regain access to the system.
Variants of Petya were first seen in March 2016, which propagated via infected email attachments. In June 2017, a new variant of Petya was used for a global cyberattack targeting Ukraine.
The new variant spreads via the [EternalBlue](https://www.wired.com/story/eternalblue-leaked-nsa-spy-tool-hacked-world/) exploit, which was used earlier in the year by the WannaCry ransomware.
Kaspersky Lab referred to this latest version as [NotPetya](https://www.wired.com/story/notpetya-cyberattack-ukraine-russia-code-crashed-the-world/) to distinguish it from the 2016 variants, due to these differences in operation. Although it claims to be ransomware, this variant was modified so that it is unable to revert its own changes and release the hard drive.
Sony
Sony’s PlayStation Network (PSN) was attacked in April 2011. This attack leaked the personal data of 77 million users. The banking information of tens of thousands of players was compromised.
After the intrusion discovery, PSN, as well as Sony Online Entertainment and Qriocity, were closed for one month. Unfortunately, in [November 2014, a subsidiary, Sony Pictures Entertainment, was attacked by malware](https://www.washingtonpost.com/news/the-switch/wp/2014/12/18/the-sony-pictures-hack-explained/).
The “Guardians of Peace” stole 100 terabytes of data, including large quantities of confidential information such as film scripts, compromising emails, and personal data of 47,000 employees.
Target
Target, the second-largest U.S. discount retail chain, was the victim of a massive cyberattack in December 2013.
Data was hijacked between November 27 and December 15 of that year. The information taken included bank card records of 40 million customers and personal data of another 70 million customers.
TJ Maxx
In March of 2007, [TJX Companies](https://www.infoworld.com/article/2202312/tjx-data-heist-confirmed-as-largest-ever.html) (parent of TJ Maxx) confirmed with the Securities and Exchange Commission that it had been attacked.
A network intrusion carried out on its systems resulted in the loss of 45.7 million consumer records, making it the most significant such breach on record at that time.
WannaCry Ransomware Attack
The [WannaCry ransomware attack](https://www.csoonline.com/article/563017/wannacry-explained-a-perfect-ransomware-storm.html) was a May 2017 worldwide cyber-event.
This attack employed the WannaCry ransomware cryptoworm which targeted devices running the Microsoft Windows operating system. It encrypted data and demanded ransom payments.
It propagated through EternalBlue; an exploit developed by the United States National Security Agency (NSA) for older Windows systems. EternalBlue was stolen and leaked by a group called The Shadow Brokers a few months before the attack.
Yahoo
In 2014, Yahoo announced it had suffered a cyberattack that [affected 500 million user accounts](https://money.cnn.com/2016/09/22/technology/yahoo-data-breach/?iid=EL), constituting the most extensive hacking of individual data directed against a single company to that date.
Names, dates of birth, telephone numbers, and passwords were taken. It is now thought that as many as [3 billion user accounts](https://money.cnn.com/2017/10/03/technology/business/yahoo-breach-3-billion-accounts/index.html) may have been affected by this attack.
---
Migrated from Apple Server Wiki. Original page ID: m105P5
# Reference: current challenges
**Current challenges**
[https://cybersecurityguide.org/resources/cybersecurity-101/](https://cybersecurityguide.org/resources/cybersecurity-101/)
**Attribution**
In what many security researchers view as a victory, albeit a small one, the security industry has made substantial improvements in the ability to assign attribution for cyberattacks.
While attribution, per se, is still challenging to achieve, vast knowledge about the [various current attack techniques](https://dl.icdst.org/pdfs/files3/db004a6f55f96c056a23fc4efc6a23ac.pdf), how they are deployed, and who uses them has been accumulated. This understanding allows researchers to make highly accurate educated guesses about the origins of an attack.
Knowing that security professionals are much better at attribution, the adversaries adapt. It is becoming more common for nation-state hackers and cybercriminals to try and imitate each other in an attempt to foil attribution efforts.
They also learn from each other to increase their capabilities. Primarily, however, their objectives remain different. Cybercriminals are generally more interested in money, while nation-state hackers are interested in stealing intellectual property and causing disruption.
While activism was once a prominent motivation for hackers, that has significantly subsided. Political and social cause activists use the Internet and modern communication tools to their great advantage but are less often seen interrupting services or exfiltrating data.
**Skills gap**
Today, we have reached the point at which cybercrime is so sophisticated that it seems nearly impossible to prevent. Scrutiny is placed on how an enterprise responds once breached – essentially a not “if” but “when” paradigm. Corporate leaders vie for the most talented [chief information security officers](https://cybersecurityguide.org/careers/chief-information-security-officer/).
These CISOs are focused mainly on organizational resiliency so they can appropriately manage events surrounding what is considered to be the inevitable data breach.
Organizations that would not have previously believed they needed a CISO are now hiring search firms to locate the best and the brightest. While the demand is high, they often require advanced infosec related degrees.
Across the board, security professionals are asked to increase their level of education, gain new skills, and hone their craft in response to the increased capabilities of their adversaries. Organizations, large and small, have accepted the fact that significant resources must be allocated to cyber defense. Security departments are enjoying a larger share of the enterprise’s budget. They can, therefore, spend more to hire people with the desired education and certifications.
[Learn more about cybersecurity certifications](https://cybersecurityguide.org/programs/cybersecurity-certifications/)
At one time, some employers were known to hire real-world hackers and convert them from the “dark side” to work for the good guys.
In recent years, however, college degrees have become near mandatory for [penetration testers](https://cybersecurityguide.org/careers/penetration-tester/), and the demand for security professionals with offensive security skills is growing every year.
The storied cybersecurity skills gap is mostly being solved by increased security budgets. While this challenge presents itself as an overwhelming shortage of people with the right cybersecurity skills, it is being solved by attracting talented, educated, and experienced IT professionals from other specialties.
**Active defensive strategies**
Cybercriminals, nation-state hackers, and hacktivists are all finding new and innovative ways to compromise digital assets. Some of the more prolific examples include:
- Using PowerPoint slides to run malicious code
- Using Microsoft Word documents to run malicious code
- Installing trojans that can use computer resources to mine cryptocurrency
- Using email spam to trick users
Many security organizations are becoming more inclined to employ defensive cybersecurity strategies.
Contrary to what some may imagine, active defensive strategies do not include attacking adversaries. Active defensive strategies are that category of strategies that include a proactive element, rather than just waiting to be attacked.
The use of pentesters or ethical hackers is an example of an active defensive strategy. These proactive activities are used to test static defenses and allow them to be fine-tuned.
[Learn more about ethical hacking](https://cybersecurityguide.org/programs/cybersecurity-certifications/ceh/)
Deception-based cybersecurity systems and processes are the best examples of active defense. A honeypot is the most basic of deception-based security.
In more sophisticated schemes, security professionals will put decoy data and what appears to be attack points all over their systems.
This strategy gives the security team the opportunity to monitor these decoy points and record the behavior of an adversary. Once the bait has been taken, the security analyst can choose to simply shut down the attack or to use [forensic analysis](https://cybersecurityguide.org/careers/digital-forensics/) to monitor the threat actor further. Since only decoy systems and data are at risk, much can be learned from the attack and then employed to protect the real data systems.
These deception-based security systems can also be used to test the organization’s playbook for automated and manual responses. These can then be updated to improve their effectiveness.
**Future of the cybersecurity industry**
**DevSecOps**
Historically security has been treated as an after-thought or, at best, a side-track. Growing cybersecurity concerns have made it essential to clarify that security controls are a vital aspect of continuous delivery.
To adapt to a philosophy that asserts that the entire development team is responsible for security, the role of DevSecOps was born.
[DevSecOps](https://www.devsecops.org/) stands for Development, Security, and Operations. Related to DevOps or SecOps, it is an idea that joins two previously separate functions into a consolidated framework.
DevSecOps teams are accountable for producing conditions for continuous secure application development. Being a newer concept than DevOps, DevSecOps underscores the importance of IT security processes and security automation in the software development lifecycle.
Conventional DevOps processes do not include security. Development without an eye toward security means that many application development ventures that practice DevOps may have no security team. Or, they may test apps only after deploying them.
This approach may cause significant delays in development and is not fit for agile DevOps practices with security included.
Going forward, security professionals need to be fully embedded in the application development process. Security professionals must learn DevOps skills, and DevOps teams must make room for these security experts.
**Artificial intelligence**
While quickly becoming an overused, and little-understood, buzzword, machine learning, and its subordinate technology of artificial intelligence, hold great promise for cybersecurity.
The ability to accurately predict future attack behavior based on historical data and identify vulnerabilities will greatly increase our defensive capabilities.
Tech writer Kayla Matthews addresses the promising use of machine learning in cybersecurity.
In her article, “*Using Machine Learning to Evaluate Cybersecurity Risk”,* she acknowledges that machine learning or artificial intelligence is no replacement for human intelligence*.
She goes on to say,
“Machine learning analyzes current and past data to identify possible weak points in a business’s cybersecurity perimeter. By pinpointing these risks, it aids information security in recognizing and resolving points of liability. This strategy also utilizes past and present information to find trends that are predictive of future occurrences. By reviewing data logs, AI finds suspicious activities and flags them as likely dangers, which cybersecurity professionals can then quarantine and investigate further.”
It is critical that [security software developers](https://cybersecurityguide.org/careers/security-software-developer/) continually upgrade their skill sets. As cyber-attacks become evermore advanced, those charged with protecting digital assets must stay one step ahead.
**Prognosis**
Governments enforce stringent regulations to protect their citizens’ privacy — regulations like the E.U. General Data Protection Regulation (GDPR) and the new California Consumer Privacy Act are raising the bar for compliance.
Cyberspace has become a digital battleground for nation-states and hacktivists. The cybersecurity industry is continually innovating. It uses advanced machine learning (ML) and AI-driven approaches to analyze network behavior and prevent adversaries from prevailing. It’s an exciting time for the industry, and looking back helps us predict where it’s going.
The prognosis for cybersecurity professionals is good – better than good. Excellent.
The other side of that coin, however, is that it is expected that threats and breaches will also increase. Most industry analysts agree that while we are not yet winning the war, we are making great strides toward shutting down all but the financially well-backed and highly educated threat actors.
Gone are the days where a credible threat is likely to be launched from the proverbial teenaged hacker working from his parent’s dingy basement.
**Conclusion**
The good guys will win. It undoubtedly doesn’t seem that way to a CISO in the throes of defending his or her systems against an aggressive cyberattack or to a CEO facing the prospect of announcing a historic data breach, but it is nevertheless true.
In the end, enterprises take whatever steps are necessary and realign whatever priorities are needed to survive, and even thrive.
The desire to be on the right side of this struggle for control in cyberspace has attracted some of the most capable minds in government, business, or academia.
Just as with physical threats, attacks, and wars, however, there will always be another threat actor scheming to exploit a perceived vulnerability for their benefit.
This condition provides thoroughly satisfying career opportunities for those with a desire to master the relevant technologies and learn the appropriate skills.
**Frequently asked questions**
**What is cybersecurity and why is important?
Cybersecurity refers to the practice of protecting computer systems, networks, and data from theft, damage, or unauthorized access. In today’s digital age, with increasing threats and sophisticated cyber-attacks, it’s crucial to safeguard personal, corporate, and government information.
**How does cybersecurity differ from information security?
While both terms are often used interchangeably, information security is a broader concept that encompasses the protection of all information, regardless of its format. Cybersecurity specifically focuses on digital data and the systems that store, process, or transmit it.
**What are the most common types of cyber threats?
Some prevalent cyber threats include malware (like viruses and ransomware), phishing attacks, denial-of-service attacks, and man-in-the-middle attacks. Regularly updating software and being cautious of suspicious emails can help mitigate these risks.
**How can I protect my personal devices and data?
Start by using strong, unique passwords for all accounts and enable two-factor authentication where possible. Regularly update software, use a reputable antivirus program, and avoid clicking on suspicious links or downloading files from untrusted sources.
**What is the role of encryption in cybersecurity?
Encryption scrambles data into a code to prevent unauthorized access. It’s vital for protecting sensitive information, especially during transmission over the internet.
**How can I recognize a phishing scam?**
[Phishing scams](https://cybersecurityguide.org/resources/phishing/) often appear as legitimate emails or messages urging you to click on a link or provide personal information. Be wary of unsolicited communications, especially those with generic greetings, spelling errors, or suspicious URLs.
---
Migrated from Apple Server Wiki. Original page ID: 5719G6Z8
# Reference: Phishing
**In this guide**
- [What is phishing?](https://cybersecurityguide.org/resources/phishing/#what)
- [Types of phishing](https://cybersecurityguide.org/resources/phishing/#types)
- [Notable attacks](https://cybersecurityguide.org/resources/phishing/#notable)
- [How to avoid phishing attacks](https://cybersecurityguide.org/resources/phishing/#avoid)
- [Conclusion](https://cybersecurityguide.org/resources/phishing/#conclusion)
- [Frequently asked questions](https://cybersecurityguide.org/resources/phishing/#faq)
Phishing is a technique widely used by cyber threat actors to lure potential victims into unknowingly taking harmful actions.
This popular attack vector is undoubtedly the most common form of social engineering—the art of manipulating people to give up confidential information— because phishing is simple and effective.
Scammers launch thousands of phishing attacks every day, and they’re often successful.
## What is phishing?
In the 1990s, it was common for [hackers](https://cybersecurityguide.org/resources/ethical-hacker/) to be called Phreaks. What passed for hacking in those days was referred to as phreaking.
So, the act of using a lure—a more or less authentic-looking email—to catch or trick an unsuspecting computer user adopted the “ph” from phreaking to replace the “f” in fishing and became modern-day phishing.
Today, the most common type of fraudulent communication used in a phishing attack is still email, but other forms of communication, such as SMS text messages, are becoming more frequent.
Threat actors use any means they can conceive to get a user to follow a link to an illegitimate webpage and enter their computer or banking system login credentials or download [malware](https://cybersecurityguide.org/careers/malware-analyst/).
In a modern phishing attack, a threat actor uses skillful social human interaction to steal or compromise sensitive information about an organization or its computer systems.
A 2021 Egress Insider Data Breach Survey has revealed that almost three-quarters (73 percent) of organizations have suffered data breaches caused by phishing attacks in the last year.
[Learn how to respond to data breaches](https://cybersecurityguide.org/resources/cyber-incident-guide/)
[Phishing scams](https://www.itgovernance.co.uk/blog/catches-of-the-month-phishing-scams-for-october-2023) are often the “tip of the spear” or the first part of an attack to hit a target. The attack may be aimed at stealing login credentials or be designed to trick a user into clicking a link that leads to deploying a payload of malware on the victim’s network.
Once one or more users within an organization fall prey to an orchestrated phishing campaign, the attackers will have culled credentials or delivered a malware payload needed to launch their full-scale attack.
There is a wide variety of attack types that begin with a phishing campaign.
The hacker’s objective may be to steal credentials and other personally identifiable information (PII) that they can then sell on the dark web, download the malware for a ransomware attack, or steal valuable information as part of an industrial or military espionage campaign.
Nation-states and state-sponsored advanced persistent threat (APT) actors use phishing to gain a presence on the victim’s network to begin privilege escalation that can eventually severely compromise our nation’s critical infrastructure or financial institutions.
Until a few years ago, it was generally pretty easy to spot a phishing email. Users could readily identify a bogus sender address, poor spelling, or a doctored link URL with only a bit of examination.
Today, scammers are much more clever. Phishing emails can be almost undetectable by the average user.
## The various types of phishing attacks
Phishing has become so profitable for bad actors that the methods for attacking various victim types have evolved. Today, there are at least four categories of phishing attacks—each with a specific victim type.
In addition to what we might think of as common phishing that is focused on everyday computer and network users, there is spear phishing, whale phishing, and smishing.
**Spear Phishing:** A more targeted form of phishing that focuses on specific individuals or organizations. Attackers often gather information about their targets to make the communication appear highly personalized and credible. For instance, an employee might receive an email seemingly from their CEO requesting an urgent wire transfer.
**Whaling:** A type of spear phishing that specifically targets high-profile individuals within an organization, such as executives or senior managers, who often have access to sensitive information and financial resources.
**Smishing (SMS Phishing):** Phishing attacks conducted via text messages. These messages often contain urgent alerts or enticing offers with malicious links. Examples include texts claiming you’ve won a prize and need to click a link to claim it, or notifications about fraudulent activity on your bank account requiring immediate action.
**Vishing (Voice Phishing):** Phishing attacks carried out over the phone. Attackers may impersonate customer service representatives, government officials, or lottery organizers to trick victims into revealing personal information or making payments.
**Social Media Phishing:** Phishers use social media platforms to send direct messages, create fake profiles, or post malicious links disguised as legitimate content or advertisements. Angler Phishing: Attackers monitor social media for users complaining about a specific company and then impersonate the company’s customer support to offer assistance, often leading to malicious links or requests for personal information.
**Pharming:** A more sophisticated attack that aims to redirect users to fake websites even if they type the correct URL. This is often achieved by compromising DNS (Domain Name System) servers or the user’s local host file.
## Notable phishing attacks
- [**Gmail Subpoena Phishing Scam (2025**)](https://nypost.com/2025/04/21/tech/gmail-users-warned-of-sophisticated-phishing-attack/?utm_source=chatgpt.com): In April 2025, a sophisticated phishing campaign targeted Gmail users by sending emails that appeared to originate from “no-reply@google.com.” These emails falsely claimed to be legal subpoenas and directed recipients to fraudulent support portals hosted on Google Sites.
- **[GrubHub Data Theft (2025)](https://about.grubhub.com/news/our-response-to-a-third-party-vendor-incident/)**: A cyberattack compromised the data of customers, drivers, and merchants associated with GrubHub, making them susceptible to phishing attempts.
- **[DISA Data Breach (2025)](https://fox59.com/business/press-releases/accesswire/998050/disa-global-solutions-inc-data-breach-under-investigation-by-levi-korsinsky-llp/)**: A US drug testing firm, DISA, reported a breach affecting 3.3 million individuals. Sensitive information, including Social Security numbers, was exposed.
- **[Hillcrest Convalescent Center Breach (2025)](https://www.hipaajournal.com/hillcrest-convalescent-center-data-breach/)**: Over 106,000 individuals had their personal and medical data compromised, potentially leading to targeted phishing attacks.
- **[Microsoft and Google Brand Phishing Attacks (2024)](https://www.infosecurity-magazine.com/news/microsoft-most-imitated-brand/)**: In the first quarter of 2024, Microsoft and Google were the most impersonated brands in phishing attacks. Microsoft accounted for 38 percent of all attempted brand phishing attempts, making it the top target, followed by Google at 11 percent. These attacks involved emails that closely mimicked official communications, luring recipients into clicking malicious links or providing sensitive information.
- **[Student Loan Forgiveness Phishing Scams (2023–2024)](https://studentaid.gov/articles/avoid-student-loan-forgiveness-scams/)**: Following the announcement of student loan forgiveness programs in the U.S., the FBI issued warnings about phishing schemes targeting borrowers. Scammers sent emails and messages impersonating official government communications, tricking individuals into providing personal and financial information under the guise of processing loan forgiveness applications.
- **[MOVEit Data Breach (2023)](https://www.ncsc.gov.uk/information/moveit-vulnerability)**: In May 2023, a critical vulnerability in the MOVEit file transfer software was exploited by the Cl0p ransomware group. While the initial breach was due to a software flaw, phishing was used to further infiltrate systems. Over 2,700 organizations were affected, and approximately 93.3 million individuals’ data were compromised, highlighting the cascading effects of combined cyberattack methods.
- **[Reddit BlackCat Attack (2023)](https://edition.cnn.com/2023/06/19/tech/reddit-hackers-demands-api/index.html)**: In February 2023, Reddit experienced a significant data breach when the ransomware group BlackCat gained access to 80GB of data. The attackers demanded a $4.5 million ransom and a rollback of planned API pricing changes. Reddit attributed the breach to a “sophisticated and highly-targeted” phishing attack against its employees.
- **[T-Mobile Data Breaches (2023)](https://www.t-mobile.com/community/discussions/accounts-services/data-breaches/42146)**: T-Mobile experienced multiple breaches in 2023, exposing customer data to phishing campaigns. These incidents highlighted vulnerabilities in corporate systems.
## How to avoid phishing attacks
[Phishing emails](https://siliconangle.com/2023/10/02/report-half-phishing-emails-now-use-obfuscation-tactics-avoid-detection/) are designed to spoof a company that potential victims are likely to be familiar with. In low-budget, widely broadcasted scams, attackers will often create an email that appears to be from a major bank or other institution, then send the email to hundreds of thousands of email addresses.
Only a percentage of the recipients will be customers of the spoofed company, but it costs the hackers nothing to play the numbers game.
They know that even if only a small percentage of the recipients are customers and only a tiny fraction of those people fall for the scam, they still come out on top.
Common phishing ploys include stating in an email that they have noticed some suspicious activity or login attempts, telling the potential victim to follow a link in the email to remedy the situation. Most of these low-budget scams are easy to detect.
There will be misspellings or language that is not consistent with a business email. The address from which the email is sent can often be identified as not belonging to the company that purports to have sent it.
Low-budget mass email scams are often targeted toward senior citizens who may not know how to detect obvious clues indicating a phishing scam.
An example of an easy-to-detect sender email address is BankofAmerica@gmail.com. To anyone familiar with email address formats and business email practices, it should be evident that Bank of America does not use a Gmail account for customer emails.
More sophisticated spear phishing and whale phishing attempts can be challenging for users to identify.
Scammers will devise URLs that look similar to the spoofed company’s legitimate email address, such as service@account.paypl.com, if they are attempting to persuade victims that the email is from PayPal.
> The cardinal rule for avoiding phishing scams is never to click a link in an email unless you are sure the email is from someone you trust. Most companies will not ask their customers to click a link in an email.
If a company asks you to interact with them on their website, type the company’s known URL directly into your browser rather than using a link from an email.
Email spam filters are an effective—but not foolproof—tool for protecting against low-budget phishing attacks.
A spam filtering solution integrated with your email platform uses a set of rules to determine which of your incoming messages are spam and which are legitimate.
The several types of spam filters include content filters, header filters, blacklist filters, permission filters, and challenge-response filters. Each applies a different set of rules to your incoming emails and can be beneficial in detecting phishing scams.
Cyber threat actors are always finding new and innovative ways to bypass spam filters to trick email or SMS users, enabling them to steal sensitive information or deliver destructive payloads. Beyond spam filters, there are steps that users should take to avoid becoming a victim of a phishing attack.
Use security antivirus and other appropriate security software on all digital devices, including mobile phones, and apply automatic update settings to ensure you have the most current protection.
For all accounts that contain sensitive information, use multi-factor authentication if available. This extra level of protection ensures that even if you fall victim to a credential-culling phishing scam, the bad actors will be unable to access your accounts.
Always back up your data. Phishing is a common prelude to a ransomware attack.
You can mitigate the adverse effects of having your data encrypted in a ransomware attack by maintaining a current backup.
[Learn more about internet safety](https://cybersecurityguide.org/resources/internet-safety/)
## Conclusion
Phishing is but a modern twist to any number of age-old ploys to trick people into giving up information that can be used against them.
From eavesdropping to mail tampering, criminals have always sought to steal information as a precursor to launching other exploits.
As it has always been, each individual must shoulder the responsibility to protect themselves from trickery and deception.
> There are software tools, such as spam filters and antivirus software, that can help, but in the end, we must all be ever-diligent and even a little suspicious of email and SMS communications.
## Frequently asked questions
**What is a phishing attack?**A phishing attack is a malicious attempt by cybercriminals to deceive individuals into sharing sensitive information, such as passwords, credit card numbers, or Social Security numbers, by posing as a trustworthy entity, often via email or other online communication methods.
**How can I recognize a phishing email?**Look for suspicious email addresses, spelling errors, generic greetings, unexpected attachments, and urgent or threatening language. If something feels off, trust your instincts.
**Are phishing attacks limited to emails?**No, phishing attacks can also occur through phone calls, text messages, social media, and fake websites. Always be cautious of unsolicited communications.
**What should I do if I receive a phishing email?**Do not click on any links, download attachments, or provide any personal information. Report the email to your IT department or email provider and delete it immediately.
**How can I protect myself from phishing attacks?**Always verify the sender’s identity, especially if they request sensitive information. Use two-factor authentication, keep your software updated, and never enter personal information into a website unless you’re certain it’s legitimate.
**Are there tools to help protect against phishing?**Yes, many email providers offer built-in phishing filters. Additionally, there are specialized security software and browser extensions designed to detect and block phishing attempts.
**How do cybercriminals benefit from phishing attacks?**Cybercriminals use the stolen information for various illegal activities, including identity theft, financial fraud, or even selling the data on the dark web.
## Sources
- 5 Most Common Types of Phishing Attack \| From [IT Governance Europe](https://www.itgovernance.eu/blog/en/the-5-most-common-types-of-phishing-attack) in Apr 2025
- Gmail Phishing Attack \| Sourced from [New York Post](https://nypost.com/2025/04/21/tech/gmail-users-warned-of-sophisticated-phishing-attack/?utm_source=chatgpt.com) in Apr 2025
- Top Phishing Attacks in 2024 \| Sourced from [Keepnet Labs](https://dmarcreport.com/blog/top-phishing-attacks-in-2024-so-far/?utm_source=chatgpt.com) in Apr 2025
- DISA Data Breach \| Sourced from [Fox59 News](https://fox59.com/business/press-releases/accesswire/998050/disa-global-solutions-inc-data-breach-under-investigation-by-levi-korsinsky-llp/) in Apr 2025
- Latest Figures and Trends \| Sourced from [StationX](https://www.stationx.net/phishing-statistics/?utm_source=chatgpt.com) in Apr 2025
- MOVEit Data Breach \| Sourced from [National Cyber Security Centre](https://www.ncsc.gov.uk/information/moveit-vulnerability) in Apr 2025
---
Migrated from Apple Server Wiki. Original page ID: n2C2K1U2
# Reference: Student Safety
[https://cybersecurityguide.org/resources/internet-safety/](https://cybersecurityguide.org/resources/internet-safety/)**In this guide**
- [Common Problems](https://cybersecurityguide.org/resources/internet-safety/#common)
- [Security Tips for Students](https://cybersecurityguide.org/resources/internet-safety/#tips)
- [Internet Safety Resources](https://cybersecurityguide.org/resources/internet-safety/#essential)
- [Conclusion](https://cybersecurityguide.org/resources/internet-safety/#conclusion)
- [Checklist for Students](https://cybersecurityguide.org/resources/internet-safety/#checklist)
- [FAQ](https://cybersecurityguide.org/resources/internet-safety/#faq)
The internet now serves as the backbone of modern education, intricately woven into every part of a student’s academic path.
Whether it’s exploring expansive online resources, engaging in collaborative projects, joining virtual classrooms, or connecting with peers worldwide, the digital world offers remarkable opportunities for learning and growth. Yet, with this level of integration comes a complex network of security risks that students must learn to navigate wisely.
Navigating this digital maze safely requires more than just common sense; it demands a comprehensive understanding of potential threats, proactive security practices, and awareness of the resources available to safeguard your digital well-being.
## Related resources
- [How to respond to cyberattacks and security breaches](https://cybersecurityguide.org/resources/cyber-incident-guide/)
- [How to spot and protect yourself from a phishing attack](https://cybersecurityguide.org/resources/phishing/)
- [What small businesses need to know about cybersecurity](https://cybersecurityguide.org/resources/small-business/)
- [Holiday hacks: Online shopping and security study](https://cybersecurityguide.org/resources/holiday-hacks/)
- [A Podcast interview with Paul Warner](https://cybersecurityguide.org/expert-interviews/paul-warner/)
## Common Internet Security Problems for Students
Students face a unique set of internet security challenges, often stemming from a combination of their online activities, technological familiarity, and potential vulnerabilities.
The compiled listings below highlight several overlapping internet safety concerns from both [Liquid Web](https://www.liquidweb.com/blog/most-common-web-security-problems/) and [Kaspersky](https://www.kaspersky.com/resource-center/threats/top-seven-dangers-children-face-online) articles, which specifically address the dangers children face online:
**Phishing and Social Engineering Attacks Targeting Students**
- Cybercriminals often craft sophisticated phishing emails disguised as university communications, financial aid notices, or even messages from professors.
- These attacks aim to steal login credentials, financial information, or sensitive personal data.
- Social engineering tactics can also exploit students’ trust and desire to help, leading them to click on malicious links or share confidential information.
**Malware Infections Through Educational Resources**
- Downloading files from unverified sources, clicking on suspicious links within online learning platforms, or using infected USB drives can introduce malware (viruses, worms, ransomware, spyware) onto personal devices, potentially compromising academic work and personal data.
**Privacy Violations on Educational Platforms and Social Media**
- Over-sharing personal information on social media profiles or within online learning environments without understanding privacy settings can expose students to risks like identity theft, stalking, or reputational damage.
- Data breaches on educational platforms can also expose student records.
**Cyberbullying and Online Harassment**
- While often considered a separate category, cyberbullying has significant security implications, affecting a student’s mental health, academic performance, and overall well-being.
- Can involve the spread of private information, harassment through various online channels, and online shaming.
**Insecure Use of Public Wi-Fi on Campus and Elsewhere**
- Connecting to unsecured public Wi-Fi networks without a VPN can expose your online activity to eavesdropping, allowing malicious actors to intercept sensitive data like login credentials and browsing history.
**Compromised Student Accounts**
- Weak or reused passwords make student accounts easy targets for hackers.
- Once an account is compromised, attackers can access personal information, academic records, and even use the account to spread malware or launch further attacks.
**Lack of Awareness Regarding Emerging Threats**
- Students may be less familiar with newer security threats like cryptojacking (where your device’s resources are used to mine cryptocurrency without your consent) or attacks targeting Internet of Things (IoT) devices connected to their home or dorm networks.
## Internet Security Tips for Students
Navigating the digital maze safely requires adopting proactive security habits:
**Mastering Password Management**
- **Create Strong, Unique Passwords:** Use a combination of uppercase and lowercase letters, numbers, and symbols for each online account. Avoid using personal information or common words.
- **Utilize a Password Manager:** Consider using a reputable password manager to securely store and generate complex passwords, reducing the need to remember multiple credentials.
- **Enable Multi-Factor Authentication (MFA):** Activate MFA whenever available. This adds an extra layer of security by requiring a second verification step (e.g., a code from your phone) in addition to your password.
**Practicing Phishing Awareness:**
- **Be Skeptical of Unsolicited Communications:** Exercise caution with emails, messages, or calls from unknown senders or those requesting personal information.
- **Verify Suspicious Requests:** If you receive a communication that seems unusual or urgent, especially from an institution, verify its legitimacy through official channels (e.g., contacting the university directly via phone or their official website).
- **Hover Before Clicking:** Before clicking on any link, hover your mouse over it to preview the actual URL. Be wary of links that look suspicious or don’t match the sender’s domain.
- **Never Share Sensitive Information Via Email:** Legitimate organizations will rarely ask for sensitive information like passwords or social security numbers via email.
**Securing Your Devices**
- **Install and Maintain Antivirus and Anti-Malware Software:** Use a reputable security suite and keep it updated to protect against the latest threats.
- **Keep Your Software Updated:** Regularly update your operating system, web browsers, and other applications to patch security vulnerabilities.
- **Enable Firewall Protection:** Ensure your device’s firewall is turned on to block unauthorized access.
- **Be Cautious with External Devices:** Scan USB drives and other external storage devices for malware before opening files.
**Protecting Your Privacy Online**
- **Review Privacy Settings:** Carefully configure the privacy settings on social media platforms and online learning environments to control who can see your information.
- **Be Mindful of What You Share:** Think critically before posting personal details, photos, or location information online.
- **Limit Information Sharing:** Only provide necessary information when signing up for online services.
- **Use Secure Browsing Practices:** Look for “HTTPS” at the beginning of website URLs and a padlock icon in the address bar, indicating a secure connection.
**Navigating Public Wi-Fi Safely:**
- **Use a Virtual Private Network (VPN):** A VPN encrypts your internet traffic, protecting your data when using public Wi-Fi.
- **Avoid Sensitive Transactions:** Refrain from accessing banking websites or making online purchases on unsecured public networks.
- **Enable Wi-Fi Auto-Connect with Caution:** Disable automatic Wi-Fi connection to prevent your device from automatically connecting to potentially malicious networks.
**Practicing Safe Social Media Habits:**
- **Be Aware of Your Digital Footprint:** Understand that everything you post online can be permanent and may be viewed by others in the future.
- **Be Respectful Online:** Engage in civil and respectful online interactions to avoid cyberbullying and harassment.
- **Report Cyberbullying and Harassment:** If you or someone you know is experiencing cyberbullying, report it to the platform administrators and a trusted adult.
**Understanding Data Backups**
- **Regularly Back Up Your Important Files:** Create backups of your academic work and personal data to an external hard drive, cloud storage, or another secure location to prevent data loss in case of device failure or malware attacks.
## Essential Internet Safety Resources
Navigating the digital world securely doesn’t mean going it alone. Numerous resources are available to provide guidance and support:
**University/College IT Security Departments**
- **Security Awareness Training:** Workshops, online modules, and guides on common threats and best practices.
- **Software and Tools:** Some universities offer free or discounted antivirus software, VPN access, or password managers for students.
- **Incident Response Teams:** Contact information and procedures for reporting security incidents or seeking assistance if your account or device has been compromised.
- **Acceptable Use Policies:** Clear guidelines on responsible and secure use of the university’s network and resources.
**Government and Non-Profit Organizations**
- **[StaySafeOnline](https://www.staysafeonline.org/):** The National Cybersecurity Alliance (NCSA) offers a wealth of free resources, including tip sheets, infographics, and guides on various internet security topics.
- **[CISA](https://www.cisa.gov/):** Provides comprehensive information and alerts on current cyber threats and offers practical advice for individuals.
- **[StopBullying.gov](https://www.stopbullying.gov/):** A federal government website dedicated to providing information and resources on cyberbullying prevention and response.
- **[ConnectSafely](https://connectsafely.org/):** Offers research-based safety tips and resources for teens and parents on navigating the online world safely.
**Reputable Cybersecurity Websites and Blogs**
- Staying informed about the latest threats and security news is crucial. Follow reputable cybersecurity websites and blogs (e.g., [Krebs on Security](https://krebsonsecurity.com/), [The Hacker News](https://thehackernews.com/), [Dark Reading](https://www.darkreading.com/)) to stay up-to-date.
**Trusted Software and Service Providers**
- Choose reputable antivirus software, VPN providers, and password managers from well-established companies with a strong track record of security and privacy.
**Educational Platforms**
- Websites like [Common Sense Education](https://www.commonsense.org/) offer digital citizenship curricula and resources that include valuable information on online safety and security.
## **Cyber Hygiene Checklist for Students**
> Protecting yourself online doesn’t have to be complicated. This [Infosecurity Europe article](https://www.infosecurityeurope.com/en-gb/blog/guides-checklists/10-everyday-practices-to-enhance-digital-security.html) breaks down easy habits to help you stay secure in the digital world.
TASK
FREQUENCY
WHY IT’S IMPORTANT
Back-up files
Every 3–6 months
Reduces the risk of compromised accounts, especially if a breach occurs on a service you use.
Run antivirus scans
Weekly
Detects and removes malware that may have unknowingly infected your devices.
Update software
As soon as updates are available
Patches security vulnerabilities that cybercriminals can exploit.
Back up files
Weekly/monthly
Prevents data loss due to device failure, malware attacks, or accidental deletion
Review privacy settings
Every semester
Ensures you are controlling who can see your information and limits unnecessary data sharing
## Conclusion
Internet security in the student context is not a one-time fix but an ongoing process of learning, adapting, and practicing safe online habits.
By understanding the common threats, implementing essential security tips, and leveraging the wealth of available resources, you can navigate the digital maze with confidence and resilience.
Remember, your digital safety is your responsibility, and the knowledge and tools to protect yourself are readily available. Stay informed, stay vigilant, and fortify your digital fortress.
## Frequently asked questions
**Why is internet safety crucial for students?**With the increasing reliance on online platforms for education, communication, and recreation, students are exposed to various risks such as cyberbullying, privacy breaches, and exposure to inappropriate content. Internet safety equips students with the knowledge and tools to protect themselves online.
**How can students protect their personal information online?**The article suggests methods like using strong, unique passwords, enabling two-factor authentication, being cautious about sharing personal details on social media, and understanding the privacy settings of online platforms.
**How can parents and educators be involved in promoting internet safety?**The article emphasizes the role of parents and educators in guiding students, monitoring their online activities, setting boundaries, and using parental control tools. It also suggests workshops and training sessions for parents and teachers.
**What should students do if they encounter cyberbullying?**Students are advised to gather evidence by taking screenshots, not responding to the bully, reporting the incident to the platform, informing a trusted adult, and, if severe, contacting local law enforcement.
**Are there any tools or apps recommended for students to ensure their online safety?**Several apps and tools are designed for student safety, such as VPN services, encrypted messaging apps, and digital safety quizzes to test their knowledge.
## Sources
- 15 common web cyber security issues \| Sourced from [Liquid Web](https://www.liquidweb.com/blog/most-common-web-security-problems/) in Apr 2025
- Internet Safety for Kids \| Sourced from [Kaspersky.com](https://bookstack.kamuela.org/resource-center/threats/top-seven-dangers-children-face-online) in Apr 2025
- 10 Practices for Enhancing Your Digital Security \| Sourced from [Infosecurity Europe](https://www.infosecurityeurope.com/en-gb/blog/guides-checklists/10-everyday-practices-to-enhance-digital-security.html) in Apr 2025
---
Migrated from Apple Server Wiki. Original page ID: Y337C7o0
# Reference: websites
[https://www.youtube.com/watch?v=HSRghjwTTOQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=8](https://www.youtube.com/watch?v=HSRghjwTTOQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=8)
Ep 8:
python -m http.server
localhost:8000
python -m http.server:7600
(note no index.html)
php -S 127.0.0.1:8085
npx http-server -p 8086
systemctl start apache2
sudo nano /etc/apache2/ports.conf
(change 80 to something else)
curl (client URL)
curl localhost:7600
curl -o coolwebsite localhost:8080
cat coolwebsite
curl -I localhost:8080. (header only)
clear
curl -v localhost:8080
request and response
wget localhost:7600
---
Migrated from Apple Server Wiki. Original page ID: F0A1L4f2
# Module 8.1: Linux for hackers: Parrot OS
Parrot OS
Hackthebox Network Chuck
[https://www.youtube.com/watch?v=HSRghjwTTOQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=8](https://www.youtube.com/watch?v=HSRghjwTTOQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=8)
Ep: 1: hack the box intro
[https://www.youtube.com/watch?v=VbEx7B\_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL)
[0:00](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=1) ⏩ Intro
[1:13](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=1&t=73s) ⏩ FREE HACKING LAB (linux)
[2:40](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=1&t=160s) ⏩ What is Linux?
[5:22](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=1&t=322s) ⏩ Introducing the Linux Terminal
[6:11](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=1&t=371s) ⏩ Linux Command: pwd
[6:55](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=1&t=415s) ⏩ Linux Command: ls
[7:33](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=1&t=453s) ⏩ Linux Command: cd
[10:01](https://www.youtube.com/watch?v=VbEx7B_PTOE&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=1&t=601s) ⏩ Test your skills
<take notes on what you see and do, email to Dr. Bill>
```
linux kernel vs. Parrot OS open source, fast, secure terminal-command line pwd print working directory ls list cd change directory cd .. cd up / root directory ls root directory
```
Ep 2: file systems
[https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2)
<take notes on what you see and do, email to Dr. Bill>
[0:00](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2) ⏩ Intro
[0:55](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=55s) ⏩ access your FREE HACKING LAB (linux)
[1:39](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=99s) ⏩ NEW COMMAND: whoami?
[2:02](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=122s) ⏩ 10 second review
[2:28](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=148s) ⏩ the ROOT of the File System
[2:45](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=165s) ⏩ NEW COMMAND: clear
[3:03](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=183s) ⏩ EVERYTHING is a file!!
[3:40](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=220s) ⏩ /bin
[4:49](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=289s) ⏩ NEW COMMAND: cat
[5:43](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=343s) ⏩ NEW COMMAND: cp
[7:12](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=432s) ⏩ NEW COMMAND: rm
[7:25](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=445s) ⏩ i DELETED a command!!!
[8:48](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=528s) ⏩ /sbin
[9:27](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=567s) ⏩ NEW COMMAND: adduser
[10:11](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=611s) ⏩ /usr
[11:32](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=692s) ⏩ NEW COMMAND: which
[12:47](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=767s) ⏩ /boot
[12:52](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=772s) ⏩ /var
[12:58](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=778s) ⏩ /tmp
[13:04](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=784s) ⏩ /lib
[13:12](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=792s) ⏩ /home
[13:40](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=820s) ⏩ /root
[14:10](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=850s) ⏩ /dev
[15:33](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=933s) ⏩ /etc
[17:11](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=1031s) ⏩ /mnt and /media
[19:24](https://www.youtube.com/watch?v=A3G-3hp88mo&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=2&t=1164s) ⏩ CHALLENGE
```
bin directory clear, ctrl-L cat cp sudo cp ls networkchuck (copied ls to networkchuck command) sudo rm ls ls is now gone sudo cp networkchuck ls cat cat cd .. ls sbin (only admin commands) sudo adduser superben cd usr ls (usr commands) which ls which cat. (where are they?) local (your command binaries) lib (your libraries) back to root— boot (startup) var (logs) home root home is different, in root directory devices are files-hard to imagine cd dev vda vdb also sda or sd1 cat devices…. sudo cat vda ctrl-c (cancel) why? corrupt files, malware etc (network settings) cd etc cd network sudo cat interfaces mnt and media media (usb drives) mnt (things you mount-file servers)
```
Ep: 3:
[https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3)
[0:00](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3) ⏩ Intro
[1:26](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3&t=86s) ⏩ FREE Linux LAB
[2:17](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3&t=137s) ⏩ Getting to know the Linux Terminal
[4:01](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3&t=241s) ⏩ NEW COMMAND: PS
[7:13](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3&t=433s) ⏩ !!!! NEW COMMANDSSSS !!!!
[8:19](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3&t=499s) ⏩ HELP!! (how to get help) MAN and -h
[9:57](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3&t=597s) ⏩ NEW COMMAND: apropos
[10:56](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3&t=656s) ⏩ your homework
[11:29](https://www.youtube.com/watch?v=Y17KTiJLcyQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=3&t=689s) ⏩ QUIZ!!!
```
terminal->shell->computer bash shell ps. (shows shell along with other process) powershell=windows shell terminal bash shell console $ means user # means root user su root id hostname uname ifconfig ip netstat ps who env lsblk lsusb lsof (open files) man pages q to quit uname -h (help) apropos (command or thing)
```
Ep. 4: managing users
[https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4)
[0:00](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4) ⏩ Intro
[1:50](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=110s) ⏩ FREE Linux LAB
[2:26](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=146s) ⏩ the Linux User
[3:11](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=191s) ⏩ UNDER ATTACK!!
[3:49](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=229s) ⏩ NEW COMMAND: adduser
[5:10](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=310s) ⏩ How to find users in Linux
[6:00](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=360s) ⏩ exploring /etc/passwd
[6:25](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=385s) ⏩ the /etc/shadow file
[7:50](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=470s) ⏩ NEW COMMAND: useradd
[9:16](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=556s) ⏩ NEW COMMAND: passwd
[10:30](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=630s) ⏩ NEW COMMAND: usermod
[13:05](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=785s) ⏩ the SUDO command
[14:20](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=860s) ⏩ NEW COMMAND: su
[16:03](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=963s) ⏩ the sudoers file
[16:21](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=981s) ⏩ NEW COMMAND: visudo
[19:10](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=1150s) ⏩ NEW COMMAND: userdel
[20:06](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=1206s) ⏩ NEW COMMAND: groupadd
[20:41](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=1241s) ⏩ exploring /etc/group
[21:27](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=1287s) ⏩ NEW COMMAND: groups
[22:20](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=1340s) ⏩ let's break the sudoers file
[23:39](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=1419s) ⏩ NEW COMMAND: usermod -aG
[25:06](https://www.youtube.com/watch?v=jwnvKOjmtEA&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=4&t=1506s) ⏩ NEW COMMAND: gpasswd
```
sudo adduser thor cat /etc/passwd passwords in /etc/shadow sudo cat /etc/shadow UID and GID home directory useradd (simple) sudo passwd user ls -la usermod -h sudo usermod ironman —shell /bin/bash sudo usermod -l tonystark ironman sudo useradd hulk -m su (switch user) sudo su - (makes you root) exit or ctrl -d sudoers file—-> sudo visudo (add sudo user) name ALL = ALL sudo userdel sudo groupadd cat /etc/group
```
Ep 8:
[https://www.youtube.com/watch?v=HSRghjwTTOQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=8](https://www.youtube.com/watch?v=HSRghjwTTOQ&list=PLIhvC56v63IJIujb5cyE13oLuyORZpdkL&index=8)
```
python -m http.server localhost:8000 python -m http.server:7600 (note no index.html) php -S 127.0.0.1:8085 npx http-server -p 8086 systemctl start apache2 sudo nano /etc/apache2/ports.conf (change 80 to something else) curl (client URL) curl localhost:7600 curl -o coolwebsite localhost:8080 cat coolwebsite curl -I localhost:8080. (header only) clear curl -v localhost:8080 request and response wget localhost:7600
```
---
Migrated from Apple Server Wiki. Original page ID: x9L3H542
# Module 8.0: Bandit wargame challenge
[https://overthewire.org/wargames/bandit/](https://overthewire.org/wargames/bandit/)
---
Migrated from Apple Server Wiki. Original page ID: G1j9x5o
# Security breach game
This is all about real people losing things that matter
Each group of 3–4 students gets one scenario card and answers four questions:
1. What happened? (the impact)
2. How did they get in? (the vulnerability)
3. What clue would tell us? (diagnostic evidence/logs)
4. How could it have been prevented? (defense)
The Security Breach CardsCard 1 — HospitalVictim
A regional hospital.
What happened?
Doctors cannot access patient records.
Surgeries are delayed.
Ambulances are diverted.
Impact
- Patient safety
- Financial loss
- Public trust
Vulnerability
Employees clicked a phishing email containing ransomware.(dancing cats?)
Diagnostic clues
- Files suddenly renamed
- Computers display ransom notes
- Security logs show one employee account accessed hundreds of files
Prevention
- Email filtering
- Employee training
- Offline backups
- Multi-factor authentication
Card 2 — AirlineVictim
Major airline.
What happened?
Reservation system crashes.
Thousands of flights delayed.
Impact
- Lost revenue
- Angry passengers
- Operational disruption
Vulnerability
Administrator password reused from another breached website.
Diagnostic clues
- Successful login from another country
- Password used correctly
- New administrator account created
Prevention
- Unique passwords
- MFA
- Login alerts
Card 3 — Personal SavingsVictim
College student.
What happened?
Bank account emptied.
Impact
- Financial loss
- Identity theft
Vulnerability
Fake banking website captured username and password.
Diagnostic clues
- Login from unfamiliar location
- Password reset email
- Transfer to unfamiliar account
Prevention
- MFA
- Verify URLs
- Password manager
- Passkeys
Card 4 — SchoolVictim
High school.
What happened?
Grades changed.
Impact
- Academic integrity
- Parent complaints
Vulnerability
Teacher password written on sticky note.(yes, this happened at HPA)
Diagnostic clues
- Grade changes after school hours
- Login from classroom computer (why are the dorms physically separate from the campus?)
- No evidence of hacking software
Prevention
- Password security
- Automatic screen locking
Card 5 — City Water SystemVictim
Municipal water utility.(check the news: this happened 7 times last week)
What happened?
Chemical settings unexpectedly changed.
Impact
- Public safety
- Service disruption (could be worse if a dam was opened)
Vulnerability
Remote access software left exposed with weak credentials.(look up SCADA)
Diagnostic clues
- Remote login
- Configuration changes
- No physical intrusion
Prevention
- VPN
- MFA
- Disable unnecessary remote access
Card 6 — Online StoreVictim
Small business.
What happened?
Customer credit cards stolen.
Impact
- Fraud
- Reputation damage
Vulnerability
Unpatched web server.(look up the US Army web hack)
Diagnostic clues
- Web logs show exploit requests
- Database queried unusually often
Prevention
- Patch management
- Web application firewall
Card 7 — Smart HomeVictim
Family.
What happened?
Security cameras accessed by strangers.
Impact
- Privacy invasion
Vulnerability
Default administrator password never changed.
Diagnostic clues
- Logins from overseas
- New unknown device connected (could be tracking passwords, etc.)
Prevention
- Change default passwords
- Firmware updates
Card 8 — FactoryVictim
Manufacturing plant.
What happened?
Production stops (look up the stuxnet case)
Impact
- Lost production (Uranium for nuclear weapons?)
- Missed customer deadlines
Vulnerability
USB flash drive infected engineering computer (stuxnet, windows updates)
- look up "air gapped computers"Diagnostic clues
- Malware appears immediately after USB insertion
- Antivirus alert
Prevention
- USB restrictions (Look up the Snowden case-how did he get data out?)
- Endpoint protection (look up Tanium)
==================== Which part failed?
- People
- Technology
- Process
Cybersecurity is almost never just about “hackers.” It usually involves weaknesses in one or more of those areas.
Threat: Something capable of causing harm.
Examples:
- Hacker
- Malware
- Fire
- Flood
- Insider
Vulnerability
A weakness that a threat can exploit.
Examples:
- Weak password
- Unpatched software
- Open Wi-Fi
- Employee mistake
Exploit
The method used to take advantage of the vulnerability.
Examples:
- Phishing email
- SQL injection
- Stolen password
Risk
The chance and consequence that a threat successfully exploits a vulnerability.
Easy mnemonicTVER
- Threat
- Vulnerability
- Exploit
- RiskThreat finds Vulnerability, uses an Exploit, creating Risk.
Another simple sentence is:
Threat + Vulnerability = Risk
with the understanding that the exploit is the mechanism connecting the two.
The CIA Triad
“What was really lost?”
- Money
- Grades
- Medical records
- Flights
Then map each answer to the CIA Triad:
Loss
CIA Property
Medical records unavailable
Availability
Grades changed
Integrity
Credit cards stolen
Confidentiality
Ransomware encrypts files
Availability
Hacker edits payroll
Integrity
Data leak
Confidentiality
---
Migrated from Apple Server Wiki. Original page ID: x3c5r5U5
# AP cybersecurity intro: CIA triad
Notes:
- intro-who
- intro-why cybersec: real people losing things that matter
- interest? code? infrastructure? policy?
- articles and notes by email: bill@hpa.edu
- HCRW text
- "Writing code itself is useless, but learning system architecture will turn you into a genius"
- FedEx sign-you will not see things the same way after this course
- First year of AP cyber (APCS)-we get to design the course-no comparison
- inventory machines-mac? M class?
- metaphors:
- highway metaphor-car is your computer, road is the internet
- house metaphor-burglars casing your neighborhood then your home
- cyberthreat game:
(syllabus is at the bottom)
Cybersecurity is about real people and the things they value, threatened by other real people
CIA Triad:
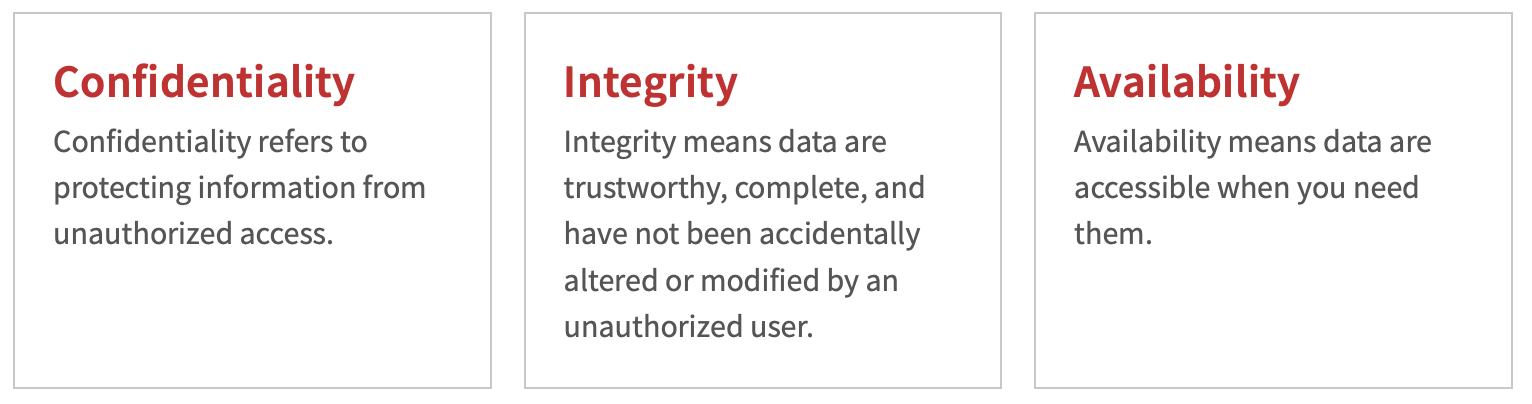Screenshot 2026-08-07 at 5.35.11 AM.png
- Confidentiality-is my stuff secret? from whom?
- Integrity-is my information intact? has it been changed?
- Availability/Access-can I access my information, my devices, my systems? Ransomware?
HPA, myHPA
- grades changed
- 24x7 operation (boarders)
- needs food and water for all
- billing locked by ransomware
- student records released
Queens Hospital
- 24 hour operation
- critical life and death consequences
- patient records are private
- surgeries cannot be delayed
- ambulances may be diverted
- many devices are internet connected (drug drips, X-rays, CT)
- patient information needs to be accessed 24x7
- patient portal needs to be accurate and open (appointments)
- older systems not hardened, little tech support
Hawaiian Airlines
- 24 hour operation (planes in the air, planes on the ground)
- ticketing, reservations must be operational
- fuel, logistics, personnel need to be in the right places
- flights delayed, customers stranded
- financial data must be confidential (competition, labor)
- tech support mainly works on web front end, not cybersec
- inbound freight and mail are delayed
Local Law firm
- sensitive information needs to be confidential (from opponents)
- financial settlements need to be private
- access to records is critical
- integrity of documents is critical (cases, agreements)
- paid tech support, maybe not on site
Kamuela Board of water supply
- 24x7 operation of water treatment and pumping
- remote control of valves, pumps and storage tanks
- regulation of critical systems (pipe pressures)
- billing needs to be private and reliable
- data on use needs to be accurate
- older remote systems (SCADA) with little tech support
Small Doctor’s office
- daily use
- HIPAA regulations (fines for each record released)
- drug prescriptions must be private and accessible
- usually little or no technical background
Personal savings account
- many home users have no tech support
- savings accounts can be emptied
- identity fraud if records are accessed
- remote control of computer can gather all passwords
Smart home
- security cameras viewed remotely
- critical devices inoperative (hot water, lighting, cooking)
- access to personal data (banking)
- little or no tech support
Young brothers barge service
- navigation disrupted-groundings
- fuel and consumables miscalculated-stranded
- scheduling and personnel disrupted
- access to financial records blocked
- access to communications blocked
- could cause disruption in life on our island (fuel, water, electricity)
Case Studies:
Screenshot 2026-08-07 at 5.27.44 AM.pngScreenshot 2026-08-07 at 5.27.55 AM.pngScreenshot 2026-08-07 at 5.28.05 AM.pngScreenshot 2026-08-07 at 5.28.15 AM.png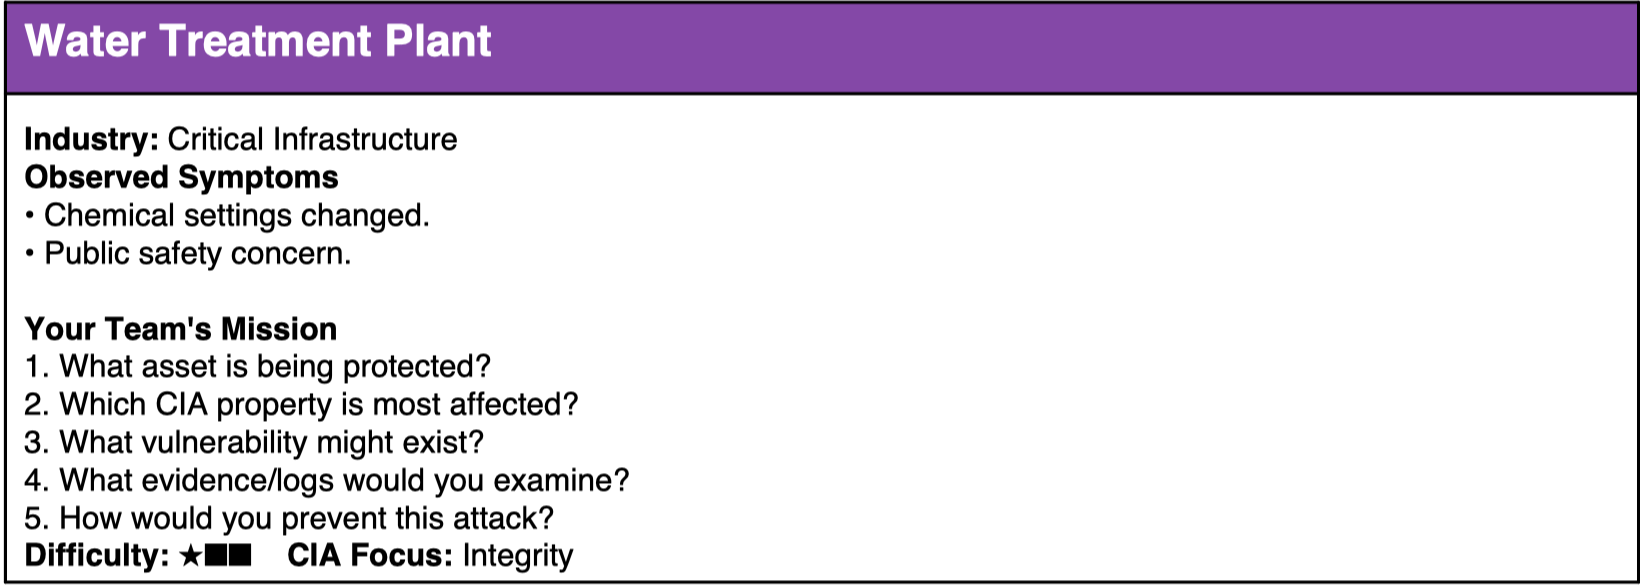Screenshot 2026-08-07 at 5.28.25 AM.png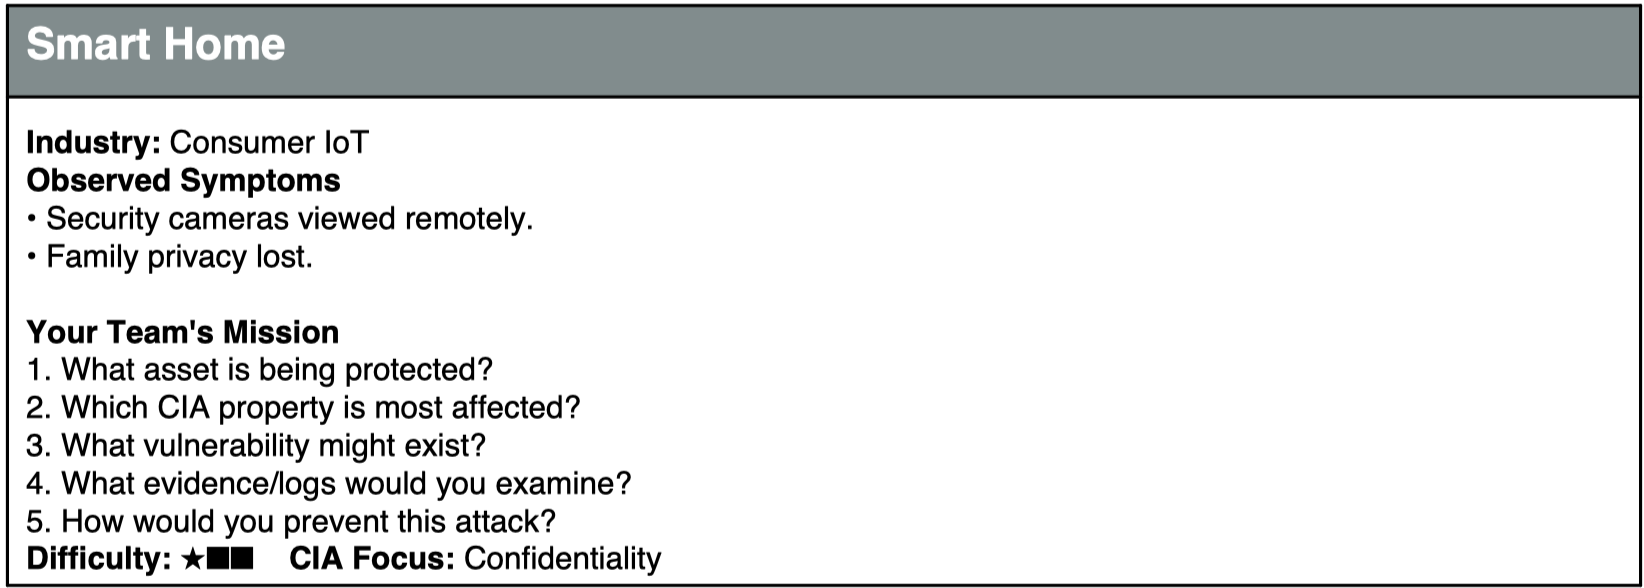Screenshot 2026-08-07 at 5.28.47 AM.png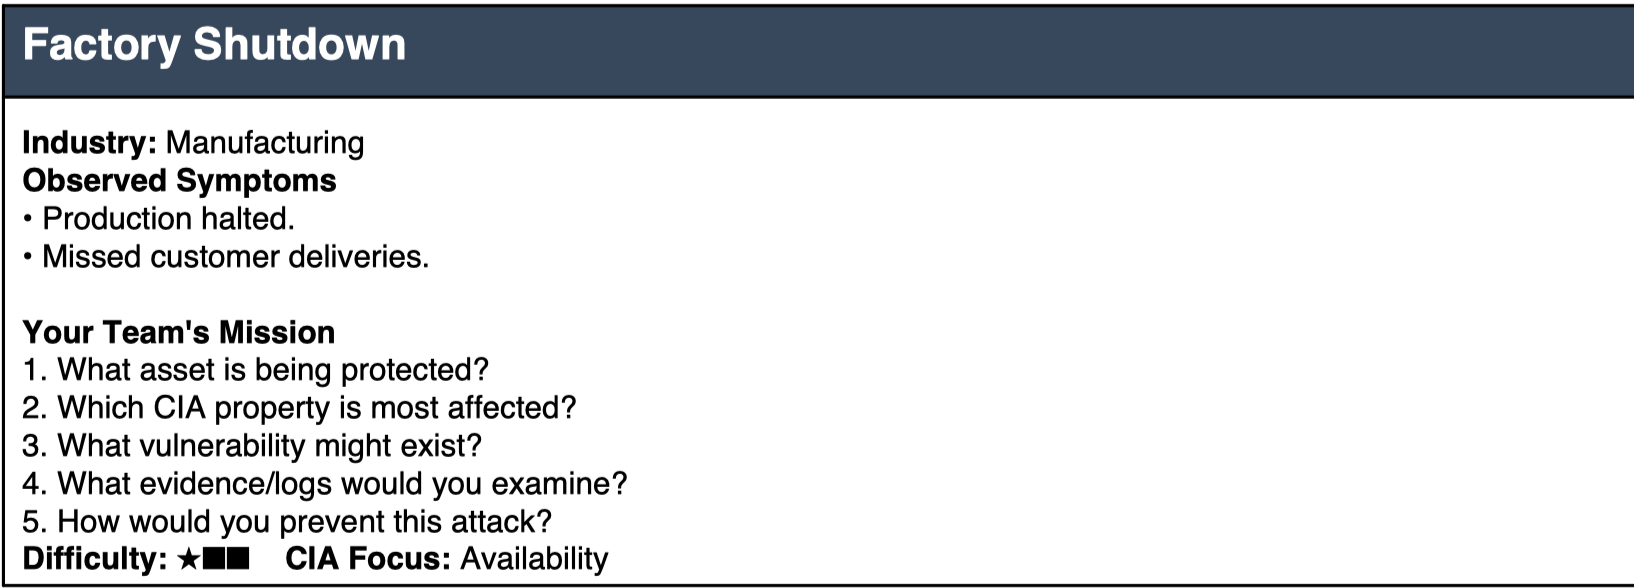Screenshot 2026-08-07 at 5.28.56 AM.png
Welcome to AP Cybersecurity!
As this is the first year we are offering this course, it will expand on our previous semester courses of Computer Engineering and Cybersecurity.
This is a fast moving topic, and I’ll be sharing articles and videos to help you keep up.
As an AP course, you know there is a GPA bump for this class, and I think we can boil down our work into three buckets:
- Homework: turned in on time for credit, half points if turned in before our next class.
- Labs: most of our work will be hands-on labs, to how we weight this may change
- Quizzes: I like to check in at the beginning of each class with a quiz, but I’m flexible on how we do this. I don’t prefer humongous tests, but as this is an AP course, we’ll be doing some evaluations from the college board to see how we are progressing.
Goals:
Our goal is safety in a digital world.
Cybersecurity is about protecting real people from other real people who want to do them harm.
Some of these “black hats” are now using AI, giving them superpowers that we will learn about.
Your superpower is the 20Watt computer you have between your ears: you are a creative, curious human, and that combination always wins out.
Much of what we will do together might seem like a detective mystery.
To use a highway metaphor-your car is your computer, your road is the internet.
Another way to look at security is protecting your house from a burglar.
To learn how to defend yourself and others in this changing landscape, we will be learning about common threats (the CIA model), and how best to protect yourself from these threats.
We’ll also create mock-attacks using “blue team vs. red team” games, which are loads of fun.
Cybersecurity exists on several levels:
- Physical: wired and wireless networks, fiber networks-how do they work, how are they vulnerable
- Logical: How does information pass through these networks: protocols, transport, machine to machine communications, hacking, code, operating systems, firewalls, Ddos, encryption, passwords, malware, clam AV,
- Social/Human: vulnerabilities, social engineering, spoofing, digital forensics, phishing, AI aided phishing, ransomware
Tools:
We will be using several levels of tools to research these, including your laptop, so we will discuss what laptop you have, and what tools you can load onto it.
Know that we will never use your laptop in an attack-defend role: your laptop is your private property, we have other machines in the elab for that.
Resources:
Along with shared articles and videos, we have several texts on pdf we will use. These can be found on the cybersecurity pages at [elab.hpa.edu](http://elab.hpa.edu), login will be shared in class.
Me:
My email is the shortest in the world: (when you run the network, you get to pick your address, one good reason to get into cybersec).
If you can email your homework before 7 PM, I can read it and give you suggestions and comments to get more points and better understand the material.
You:
How to succeed?
- Take notes in class-we may make this a graded exercise, points for notes, let’s discuss in class
- Reach out when you are stuck: you are busy, with other class loads, sports, and a vibrant social life (we hope). Let me know how I can help, that’s why I’m here.
- Collaborate: this will be your secret weapon in college, but be careful: college computer courses will fail you and send a letter to the dean if you copy work, including code. I know this first-hand. (ask).
- AI: you would not send a robot to the gym to do your workout, but it might make a helpful workout partner. Know that I use AI a great deal with my programming, but my ideas are mine. Anything you submit with your name for credit must be your thinking, not the collective slop of the silicon intelligence.
Course description: from the course catalog…
This course introduces students to the fundamentals of cybersecurity through interactive activities,
real-world case studies, and hands-on labs. Students will learn how to stay safe online, understand
how cyberattacks work, and explore careers in cybersecurity. The course builds critical thinking,
ethical awareness, and technical confidence using both unplugged and online tools.
Course Objectives:
\- Understand the core principles of cybersecurity (confidentiality, integrity, availability)
\- Identify different types of cyber threats and attacks
\- Practice safe online behaviors and password hygiene
\- Explore ethical hacking and digital forensics
\- Learn about network security, cryptography, and firewalls
\- Investigate career paths in cybersecurity
As always, reach out to me if you have any questions.
aloha
b
---
Migrated from Apple Server Wiki. Original page ID: e703f1P7
# cyber video #1 notes-Hacker History
[https://www.youtube.com/watch?v=dc6q04o8Y6o&t=1s](https://www.youtube.com/watch?v=dc6q04o8Y6o&t=1s)
[Download Cybersecurity Expert Answers Hacking History Questions Tech Support WIRED.mp4 (video/mp4, 184.2 MB)](https://bookstack.kamuela.org/attachments/340)Look up these references:
- guards, guns and gates vs now?
- CIA vs. US Army
- default passwords: [shodan.io](http://shodan.io)
- MFA and sim card swapping
- PKI basics-guessing the keys, how big?
- public, private keys, hardware keys (mac, PC)
- firewall? cars, airplanes, buildings
- surface web, deep web (95%), dark web, indexed?
- stuxnet: first logical->physical attack
- airgap-what is it?
- “those who know are not talking, those who don’t won’t shut up”
- OPM data breach-what? who? why dangerous?
- data is more valuable than oil—
- tik tok vs. cisco routers-why?
- electronic voting vs. US vs. Canada
- Wannacry malware 2017 control servers DNS
- colonial pipeline-oil ransomware $5M, SCADA attack (stuxnet, water companies)
- why bitcoin for ransomware?
- VPN-private? Hides your local IP, surfaces elsewhere
- phishing, Nigerian prince emails, spearfishing, tailgating, smishing, vishing, quishing (QR codes)
- password managers-local? cloud? passkeys? FIDO? biometrics, PKI challenge response
- antivirus-pc? mac? how different?
- CIA triad
- first virus Morris worm 1988 MIT student, see also cuckoos egg
- 2600 Hz captain krunch, 2600 magazine, steve jobs
---
Migrated from Apple Server Wiki. Original page ID: e7n7w6
# _00 class notes
8.26.26 Wednesday
On your laptop:
ethernet adapters: usb-c for laptops
email to bill@hpa.edu
quiz: 8.24.26
1. what was the speed of the ethernet cable you created?
2. as a cybersecurity expert, what are the good and bad parts of ethernet, wireless and fiber?
3. from your homework, list the IP address, subnet mask and router you found
4. list the MAC address for your computer
worksheet 8.24.26-network recon; find the intruder!
record your results and email to bill@hpa.edu
part one: arp scans, MAC addresses
1. join the cyberwifi network (password on the board)
2. run an arp -a scan
3. how many hosts do you see?
4. what is common about their MAC address? (look at the first 3 pairs)
5. look online for OUI lookup, (a wireshark utility), copy in one of the MAC addresses you found
6. what could this tell you about the intruder?
part two: nmap
1. pick one of the clients on the cyberwifi network (remember, these are your friends, be nice)
2. use nmap -sn 192.168.4.0/24 to verify the IP address for your victim
3. use nmap 192.168.4.x to scan the victim
4. what do you see?
part three: IP net monitor
1. make sure you have IP net monitor installed on your computer
2. run a bonjour scan on your network-do you see IP addresses there?
3. repeat the steps above using the Address Scan tool and port scan
Homework: 8.24.26
- Use the tools above at home/dorm and record your results so you can share with the class Wednesday
- Look on the app store for other network scanners, try a few of the free ones on your network
next:
- setup your pi server
- linux for hackers
- hcrw text
---
Migrated from Apple Server Wiki. Original page ID: w378H2o5Y
# cybersec q1 topics
Plan: Q1 (bold items are completed)
- CIA triad
- ethernet cables (the “tubes”)
- connection: 8 wires
- challenge: connection speed-iperf
- compare with fiber, wifi: security, range, speed
- homebrew: linux on owner laptops
- IPNM: gui tool
- terminal: arp -a and nmap -sn 192.168.8.0/24
- challenge: find the intruder
- nmap solo: ports
- challenge: find the doors
- network topology: /24 and /16
- IP address, gateway, subnet, DNS (more on subnet and DNS next)
- MAC address: ID of machine
- challenge: ID intruder
- OUI lookup: who is on what machine
- IPNM: bonjour scan vs address scan (scope)
- back to addresses: test at dorm, home
- ethernet adapters: usb-c for laptops, home scans on wired network: compare
- pi server stations: wifi at first, cyber5 network (192.168.8.1 with tailscale on glinet)
- change name
- join cyber5 network
- note IP address (ifconfig)
- ping gateway
- traceroute to 4.4.4.4
- challenge: ssh into other machines, then change password (share with me)
- pi scanning tools, gui?
- challenge: scan local wLAN
- navigation: network chuck videos (bring headphones)
- basic commands: ping, traceroute
- navigation: pwd, ls, cd, mkdir, touch, nano, mv, rm
- create hidden file
- ssh challenge: find the file
- navigation: wildcards, up, back, ctrl-c ctrl-z
- extended commands: nslookup, dig
- DNS and DHCP, test with IPNM
- python scripts: http server
- setup apache2
- setup network: router, inbound port mapping, AP
- security: MAC filtering
- security: client monitoring
- defense: MAC spoofing, arp cache poisoning
- defense: tcpdump
- defense: wireshark intro-packets
- defend your home project: http, ssh, ftp servers
- firewalls-intro static rules
- SPI firewalls-dynamic rules
- IP addresses → MAC addresses → ports → services → scanning → attack surface
- TCP/IP conversations
- capture, decoding PCAP
- locate, watch, attack
- simple: DDOS
- encryption of traffic
- VPN-truly safe?
- LAN VPN?
- secure web traffic: http vs. https
- content filtering: ad blocking (simple)
- linux tools: Kali linux
- passwords
- hashing
- parrot OS and Kali
- MIM wireless attacks-aircrack-ng
- malware-clam AV EICAR
- log analysis with parrot os
- privacy: VPNs and TOR
- social engineering: internal vs. external vulnerabilities
- social engineering a scammer: [https://www.youtube.com/watch?v=ec57eDghdvM](https://www.youtube.com/watch?v=ec57eDghdvM)
- privacy
- SIM swapping: [https://www.youtube.com/watch?v=64p\_WkYc9d0](https://www.youtube.com/watch?v=64p_WkYc9d0)
Case studies:
1. physical vulnerability: wifi, ethernet, KB, screenlocks, drives, backups
2. LAN security: firewalls, SPI, DPI, uPNP internal holes
3. physical hacking: stuxnet, SCADA
4. prevention: firewall, air gap, defense in depth
5. human: Snowden USB, stuxnet
6. personal: spoofed email, password entropy
7. OSINT: what is available to whom and why
8. LLL analysis of three levels: personal, small shop, enterprise
9. most common attacks: internal vs. external
10. attack detection: log analysis
11. cyberlaw: now and future TGC
12. coding and scripts
13. setup an ad blocker on rPI
14. deep fakes: PBS Hany Farid, C2PA certification
15. cryptocurrency-attacks
16. iot devices-vulnerabilities
• 17. AI enabled attacks
---
Migrated from Apple Server Wiki. Original page ID: 31z410J
# _01 references
To edit this page, click the Edit (pencil) button. To delete this page, click the Action (gear) button and choose Delete.
When you edit this page, you can easily rename the page, and use the editing toolbar to:
- Apply paragraph or character styles to text.
- Create bulleted lists, numbered lists, and tables.
- Insert media, such as images, audio, or QuickTime movies.
- Attach files.
- Insert an HTML snippet from another website or email.
For more information about editing pages, click the Action (gear) button and choose Help.
---
Migrated from Apple Server Wiki. Original page ID: H553Z1p1V
# python scanner project
sudo nano scanner.py
\# network\_scanner.py
import ipaddress
import platform
import socket
import subprocess
from concurrent.futures import ThreadPoolExecutor, as\_completed
from datetime import datetime
import pandas as pd
import psutil
import streamlit as st
COMMON\_PORTS = {
22: "SSH",
53: "DNS",
80: "HTTP",
443: "HTTPS",
445: "SMB",
3389: "RDP",
5900: "VNC",
8080: "HTTP-ALT",
}
def get\_local\_ip():
"""
Determine the primary local IPv4 address.
"""
s = socket.socket(socket.AF\_INET, socket.SOCK\_DGRAM)
try:
s.connect(("8.8.8.8", 80))
ip = s.getsockname()\[0\]
except Exception:
ip = "127.0.0.1"
finally:
s.close()
return ip
def guess\_network():
"""
Try to find the subnet/netmask associated with the primary interface.
"""
local\_ip = get\_local\_ip()
for interface, addresses in psutil.net\_if\_addrs().items():
for addr in addresses:
if addr.family == socket.AF\_INET and addr.address == local\_ip:
if addr.netmask:
network = ipaddress.IPv4Network(
f"{addr.address}/{addr.netmask}",
strict=False
)
return str(network)
# fallback
return f"{local\_ip}/24"
def ping\_host(ip):
"""
Ping host once.
"""
system = platform.system().lower()
if system == "windows":
command = \["ping", "-n", "1", "-w", "700", ip\]
else:
command = \["ping", "-c", "1", "-W", "1", ip\]
try:
result = subprocess.run(
command,
stdout=subprocess.DEVNULL,
stderr=subprocess.DEVNULL,
timeout=2,
)
return result.returncode == 0
except Exception:
return False
def resolve\_hostname(ip):
try:
hostname, \_, \_ = socket.gethostbyaddr(ip)
return hostname
except Exception:
return ""
def check\_port(ip, port, timeout=0.25):
sock = socket.socket(socket.AF\_INET, socket.SOCK\_STREAM)
sock.settimeout(timeout)
try:
return sock.connect\_ex((ip, port)) == 0
except Exception:
return False
finally:
sock.close()
def scan\_ports(ip):
open\_ports = \[\]
for port, service in COMMON\_PORTS.items():
if check\_port(ip, port):
open\_ports.append(f"{port}/{service}")
return ", ".join(open\_ports)
def scan\_host(ip):
ip = str(ip)
if not ping\_host(ip):
return None
hostname = resolve\_hostname(ip)
ports = scan\_ports(ip)
return {
"IP Address": ip,
"Hostname": hostname,
"Open Ports": ports,
"Status": "Online",
}
def scan\_network(network\_string, workers=64):
network = ipaddress.ip\_network(network\_string, strict=False)
hosts = list(network.hosts())
results = \[\]
progress = st.progress(0)
status = st.empty()
completed = 0
with ThreadPoolExecutor(max\_workers=workers) as executor:
futures = {
executor.submit(scan\_host, host): host
for host in hosts
}
for future in as\_completed(futures):
completed += 1
try:
result = future.result()
if result:
results.append(result)
except Exception:
pass
progress.progress(completed / len(hosts))
status.text(
f"Scanning {completed}/{len(hosts)} addresses..."
)
progress.empty()
status.empty()
return results
\# ------------------------------------------------------
\# STREAMLIT DASHBOARD
\# ------------------------------------------------------
st.set\_page\_config(
page\_title="Network Scanner",
page\_icon="🌐",
layout="wide",
)
st.title("🌐 Network Scanner")
st.caption(
"Discover active hosts and common network services on an authorized network."
)
default\_network = guess\_network()
with st.sidebar:
st.header("Scan Settings")
network\_input = st.text\_input(
"Network / CIDR",
value=default\_network,
help="Example: 192.168.1.0/24",
)
workers = st.slider(
"Concurrent workers",
min\_value=8,
max\_value=128,
value=64,
step=8,
)
scan\_button = st.button(
"Start Scan",
type="primary",
use\_container\_width=True,
)
st.divider()
st.write("Local IP")
st.code(get\_local\_ip())
st.write("Detected network")
st.code(default\_network)
if scan\_button:
try:
network = ipaddress.ip\_network(
network\_input,
strict=False
)
if network.num\_addresses > 1024:
st.warning(
"This dashboard limits scans to networks of "
"1024 addresses or fewer."
)
st.stop()
except ValueError:
st.error("Invalid network. Example: 192.168.1.0/24")
st.stop()
st.info(f"Scanning {network\_input}")
start = datetime.now()
results = scan\_network(
network\_input,
workers=workers
)
elapsed = (datetime.now() - start).total\_seconds()
st.session\_state\["results"\] = results
st.success(
f"Scan completed in {elapsed:.1f} seconds."
)
if "results" in st.session\_state:
results = st.session\_state\["results"\]
if not results:
st.warning("No active hosts found.")
else:
df = pd.DataFrame(results)
# sort numerically by IP
df\["\_ip\_sort"\] = df\["IP Address"\].apply(
lambda x: int(ipaddress.ip\_address(x))
)
df = (
df.sort\_values("\_ip\_sort")
.drop(columns=\["\_ip\_sort"\])
)
total\_hosts = len(df)
hosts\_with\_ports = (
df\["Open Ports"\]
.astype(bool)
.sum()
)
c1, c2, c3 = st.columns(3)
c1.metric(
"Online Hosts",
total\_hosts
)
c2.metric(
"Hosts With Open Ports",
hosts\_with\_ports
)
c3.metric(
"Network",
network\_input
)
st.subheader("Discovered Devices")
st.dataframe(
df,
use\_container\_width=True,
hide\_index=True,
)
csv = df.to\_csv(
index=False
).encode("utf-8")
st.download\_button(
"Download CSV",
csv,
"network\_scan.csv",
"text/csv",
)
pip install streamlit pandas psutil
streamlit run scanner.py
http://localhost:8501
---
Migrated from Apple Server Wiki. Original page ID: z3L1C1o972